Why in News?
The National Health Authority launched its Secure Data Environment application at Arogya Manthan on 25 September 2026 to support governed health-data research.
- NHA developed the environment with support from the Indian Institute of Science, Bengaluru.
- The announced design covers access to and analysis of AB PM-JAY and ABDM health data.
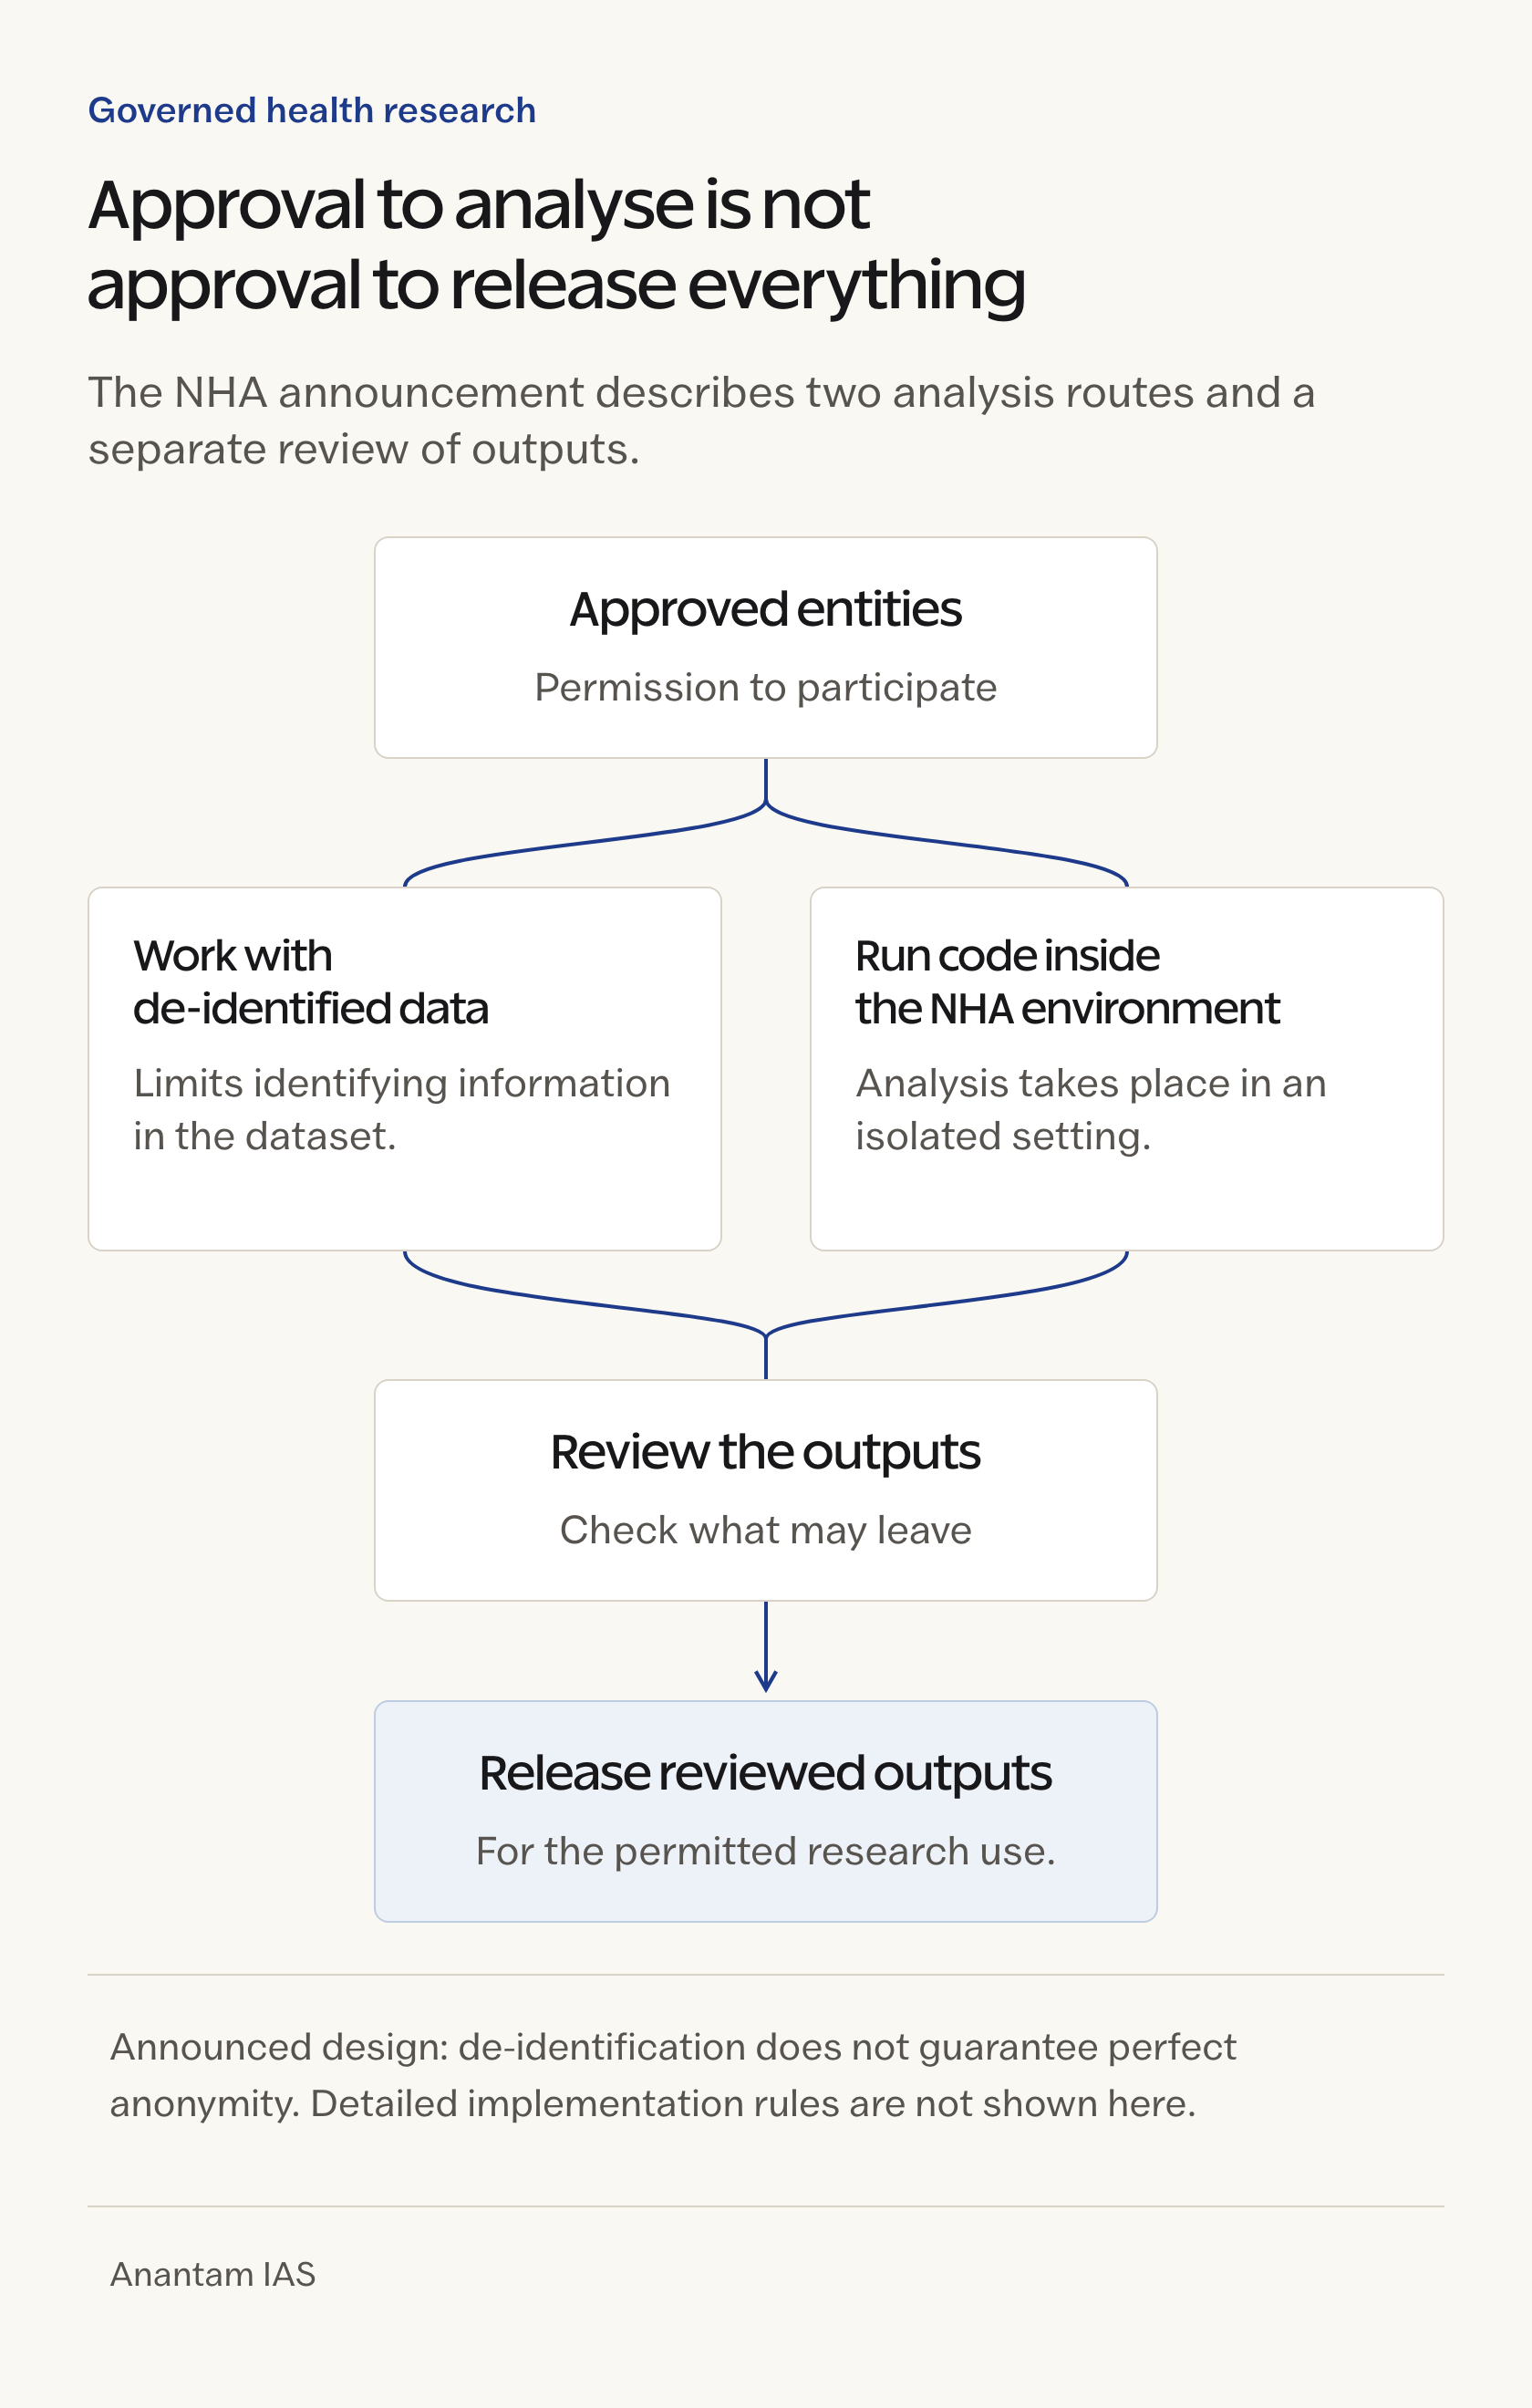
- Approved entities will work with de-identified data or execute code within an isolated NHA environment; outputs will undergo review before release.
- The release describes intended uses, including programme planning, outcome analysis and responsible AI innovation; it does not establish completed research outcomes.
- Health records can support research while revealing intimate information, making the conditions of access as important as the research objective.
- A governed environment makes the distinction between permission to analyse records and permission to release results central to data use.
UPSC Relevance
Prelims Relevance
- NHA: National Health Authority; developer of the SDE with IISc support.
- SDE: governed access to and analysis of health data.
- ABHA: digital health identity, distinct from health-assurance coverage.
- NHCX: National Health Claims Exchange for interoperable claims processes.
- De-identification: reducing identifiability, not proof of zero disclosure risk.
Mains Relevance
GS Paper 2
- Governance of sensitive health information and accountability for research access.
- Separating digital health identity, health assurance, claims exchange and research functions.
GS Paper 3
- Responsible AI research and the limits of technical safeguards.
Essay
- Public value from data depends on justified use and accountable access.
Background and Context
Different health systems serve different purposes
The SDE adds a research function to the health ecosystem; it should not be confused with an identity, insurance benefit or claims-processing service.
- AB PM-JAY is a health-assurance programme. The research value of records generated through its operation is a separate question from a beneficiary’s entitlement to treatment or the settlement of an individual hospital claim.
- ABDM supports the digital health ecosystem. Its health-data context can inform research, but the SDE announcement does not say that every linked record has already become available to every approved researcher.
- ABHA provides a digital health identity. Possessing an identifier is not the same as receiving health-assurance coverage, approving a research project or authorising unrestricted disclosure of the person’s clinical information to outside users.
- NHCX concerns standardised exchanges between participants in health-insurance processes. The SDE instead concerns governed analysis: exchanging a claim for processing and analysing health information for research have different purposes and access requirements.
- Programme planning and outcome analysis are intended research uses. For example, studying patterns of service use asks a population-level question; it does not require publishing named patient histories as the research product.
How controlled research and reviewed outputs fit together
The source describes approved participation, controlled analysis and output review; these safeguards answer different questions about who can work, how and what may leave.
- Approved entities are the intended users. Approval is an entry condition, not a declaration that everyone can browse patient records; the launch release does not detail the full application procedure or eligibility criteria.
- De-identified data is one announced route. De-identification addresses the information exposed in a research dataset; it does not, by itself, decide whether a particular organisation should receive permission to use that dataset.
- Code execution inside an isolated NHA environment is the other announced route. In this arrangement, a researcher’s analytical instructions work within a controlled setting rather than requiring unrestricted export of the underlying records.
- Output review before release creates a separate checkpoint after analysis. Permission to run a calculation does not automatically grant permission to publish or export everything it produces, including potentially revealing individual-level results.
- The PIB announcement states these mechanisms at a high level. It does not specify a particular encryption system, differential-privacy technique or output-testing threshold, so those implementation details should not be presented as established features.
Research access is neither perfect anonymity nor clinical approval
The launch establishes a direction for governed research, while operational reach, residual privacy risks and the quality of resulting evidence remain separate questions.
- De-identification should not be equated with guaranteed anonymity. A prudent governance assessment asks whether unusual combinations of information could expose someone, rather than assuming that removing direct identifiers eliminates every possible disclosure risk.
- Privacy safeguards do not establish scientific validity. A securely handled dataset can still be incomplete or unrepresentative; researchers must examine what their observations can support before applying conclusions to populations beyond the data.
- Responsible AI innovation is an intended use, not certification of a diagnostic system. Access to research data does not itself demonstrate clinical safety, effectiveness or suitability for deployment in decisions affecting patient care.
- The release calls the SDE an envisaged governed environment and describes what approved entities will be able to do. Launching the application is not evidence of universal access, completed rollout or measured patient benefits.
- Consent and lawful processing remain governance questions. Nothing in the launch announcement establishes an exemption from consent requirements, mandatory patient participation or permission to reuse health information for any purpose researchers might propose.
Way Forward
Make the research boundary accountable
- Publish clear access criteria and permitted research purposes, with responsibilities for applicants and reviewers.
- Explain output-review rules and the process for challenging a refusal without exposing sensitive records.
- Require researchers to report data limitations and distinguish exploratory findings from evidence supporting clinical use.
- Assess privacy protection and research usefulness separately, so successful access controls are not mistaken for reliable scientific conclusions.
Conclusion
- The SDE’s central idea is governed research: approved work with protected data and review before outputs leave. Its value depends on implementing those boundaries clearly, rather than treating a launch as proof that privacy risks have disappeared.
- For a governance answer, distinguish identity, health assurance, claims exchange and research access. Then assess whether access decisions, analytical methods and release checks each protect patients while allowing useful questions about healthcare to be investigated.
UPSC Practice Questions
Prelims MCQ 1
With reference to the announced NHA Secure Data Environment, consider the following statements:
- Approved entities may execute code within an isolated NHA environment.
- Research outputs are to be reviewed before release.
- The launch establishes unrestricted public access to identifiable patient records.
How many of the above statements are correct?
(a) Only one (b) Only two (c) All three (d) None
Answer: (b) Only two
Explanation:
The announcement provides for approved users, controlled analysis and reviewed outputs. It does not create unrestricted access to identifiable records.
Prelims MCQ 2
Which function most directly distinguishes NHCX from the announced Secure Data Environment?
(a) NHCX supports interoperable health-insurance claims processes. (b) NHCX certifies every research model for clinical use. (c) NHCX guarantees that de-identified data cannot reveal identity. (d) NHCX grants unrestricted public research access.
Answer: (a) NHCX supports interoperable health-insurance claims processes.
Explanation:
NHCX concerns standardised health-insurance exchanges; the SDE is intended for governed health-data research and analysis.
UPSC Mains Questions
- Explain how approved access, controlled analysis and output review address different governance risks in health-data research.
- Why should privacy safeguards in a health-data environment be assessed separately from the scientific validity and clinical usefulness of research outputs?
Source: PIB, Ministry of Health and Family Welfare.
Frequently Asked Questions
What is the NHA Secure Data Environment?
It is an application envisaged as a governed environment for accessing and analysing AB PM-JAY and ABDM health data. NHA developed it with support from IISc Bengaluru for approved research uses.
Can researchers freely download identifiable patient records?
The announcement does not provide unrestricted access to identifiable records. It describes approved entities working with de-identified data or executing code within an isolated NHA environment, with outputs reviewed before release.
Does de-identification guarantee complete anonymity?
No. De-identification reduces identifiability but should not be read as proof that disclosure is impossible. Access decisions and output review remain distinct safeguards in the announced approach to governed health-data research.
Is SDE the same as ABHA or NHCX?
No. ABHA is a digital health identity, and NHCX supports health-insurance claims exchanges. SDE concerns governed research access and analysis; permission for one function should not be assumed to authorise another.
Does the launch approve AI tools for clinical use?
No. Responsible AI innovation is an intended research use. The launch announcement does not demonstrate that any resulting model is clinically safe or effective, or that it has received approval for patient-care deployment.
Tell Google you want more of this.
Add Anantam IAS as a preferred sourceOne tap, and this site shows up more often in your own Top Stories, AI Overviews and AI Mode. Remove it any time.