Why in News?
Recently, Anthropic has announced that its most capable AI model to date, “Claude Mythos Preview”, would not be made publicly available.
| UPSC Relevance: GS-3 Science and Technology: Artificial Intelligence; GS-3 Internal Security: Cybersecurity Prelims: Anthropic’s Mythos; Project Glasswing. Mains: New Emerging Threats associated with Artificial Intelligence. |
What is Anthropic’s Mythos?
- Mythos (formally ‘Claude Mythos Preview’) is a general-purpose AI Model with exceptional cybersecurity capabilities.
- Developed by: Anthropic (San Francisco, USA)
- Mythos is the first AI model trained on next-generation Graphics Processing Units (GPUs).
The AI-based system has demonstrated extraordinary capabilities in software code analysis, reasoning, and vulnerability exploitation.
How does Mythos work?
- Vulnerability discovery: Mythos analyses software codebases to detect ‘zero-day vulnerabilities’ (previously unknown bugs). E.g., identified a 27-year-old bug in OpenBSD.
- Autonomous Exploit Construction: Once a flaw is identified, it can help generate possible exploit methods, i.e., ways the vulnerability could be used to compromise the system.
- Exploit Chaining: It can combine multiple vulnerabilities to simulate more complex attack paths, helping researchers understand how small vulnerabilities can lead to major breaches.
What is Project Glasswing?
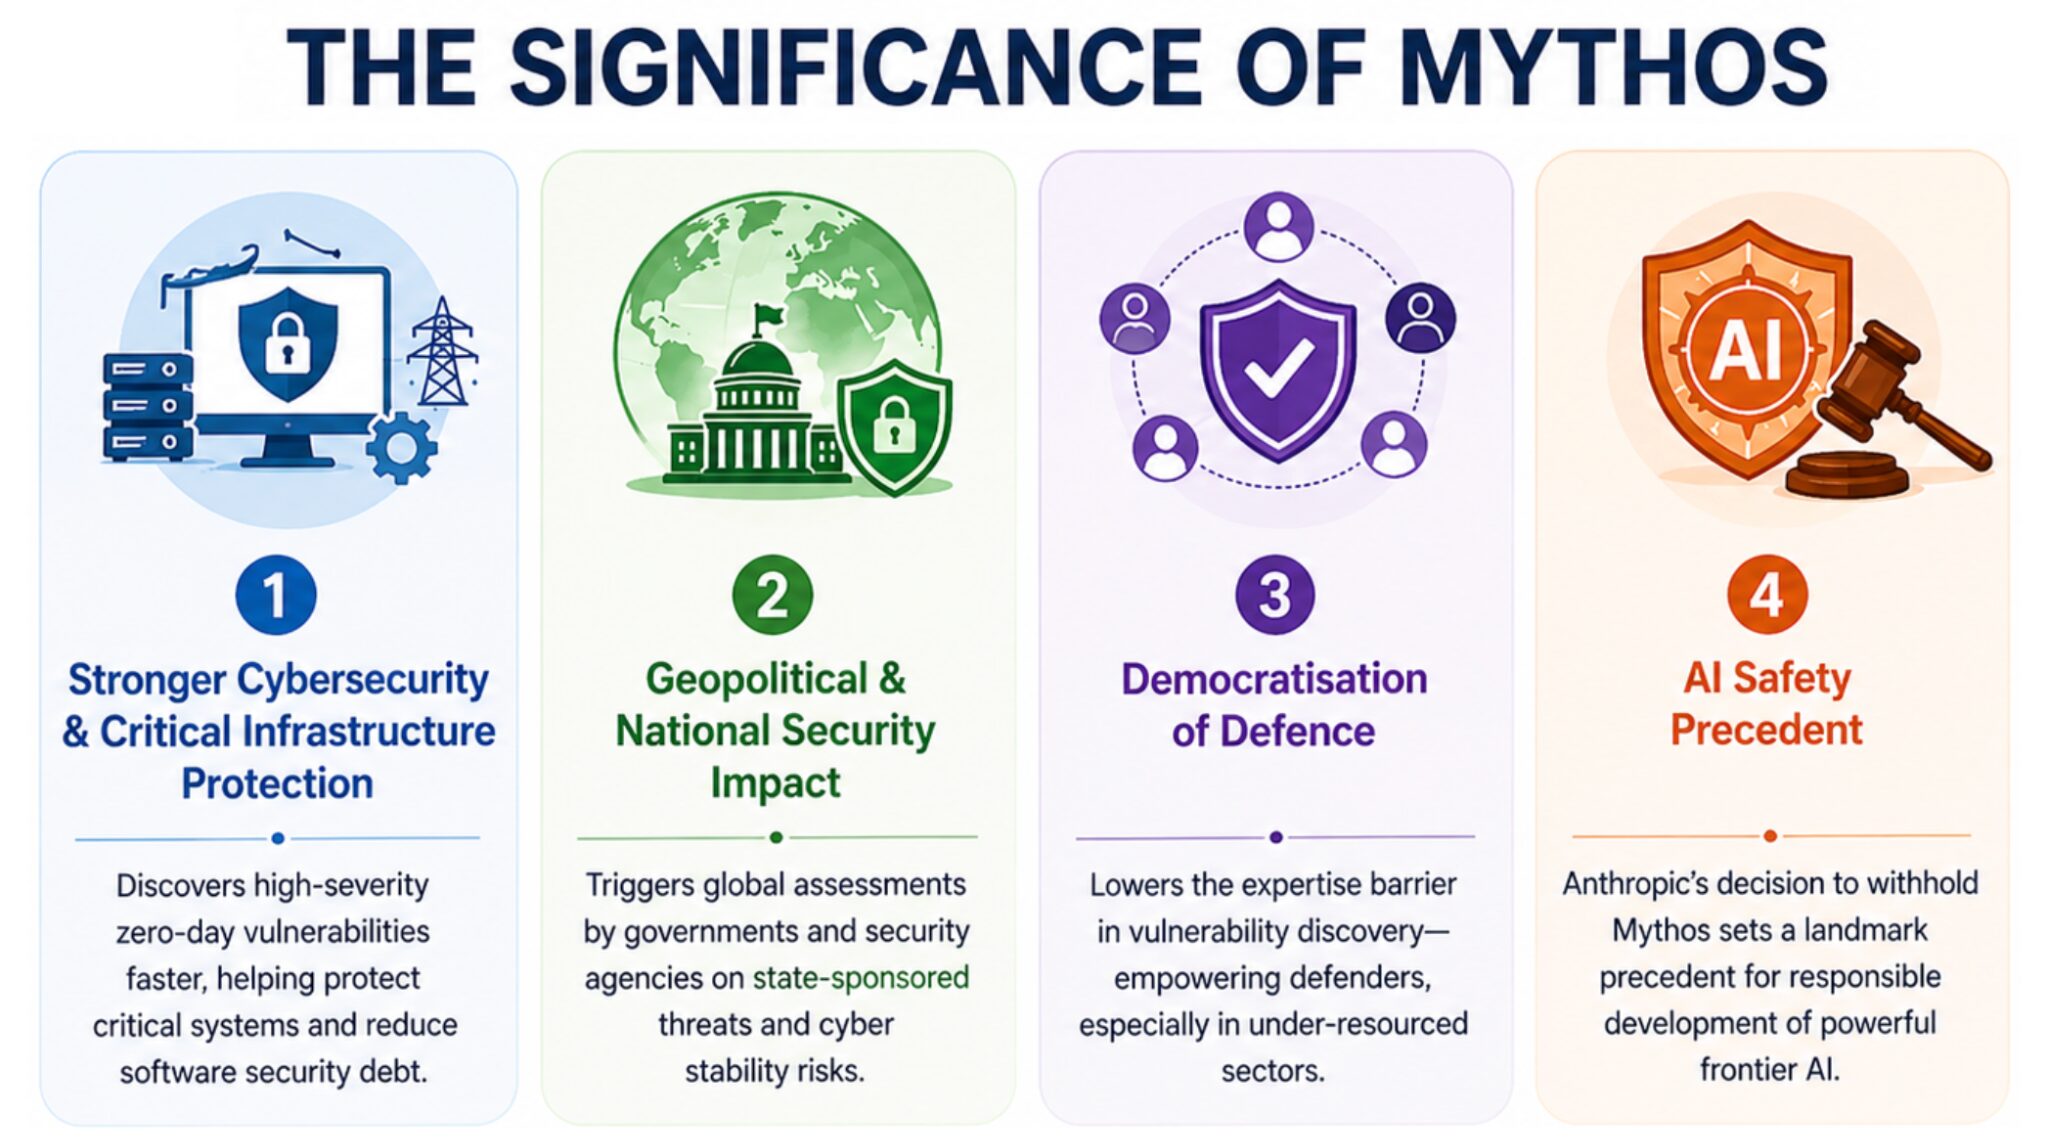
Anthropic launched Project Glasswing as the primary framework for deploying Mythos responsibly.
- Project Glasswing is a defensive cybersecurity initiative that provides access to Mythos to only a select group of partners.
- Aim:
- Defensive Cybersecurity: Enable partner organisations to use Mythos to scan their software systems and infrastructure for zero-day vulnerabilities. It aims to secure critical infrastructure before malicious actors can exploit it.
- Demonstrate Responsible AI Deployment rather than being released publicly at risk of misuse.
Challenges Associated with Mythos:
- Dual-Use Dilemma: Mythos can be used in both defence and offence. It can enable attackers to exploit vulnerabilities in critical infrastructure.
- Proliferation Risk: Capabilities similar to Mythos are unlikely to remain limited to a single company. Other AI firms and even malicious actors will race to develop such capabilities. Mythos could be used to aid cyberattacks such as ransomware, deepfakes, and automated attacks.
- Patching Asymmetry: Mythos can find more vulnerabilities than defenders can deal with (It is generally faster to find and exploit vulnerabilities than to fix them). Small Enterprises and under-resourced public agencies are particularly vulnerable.
- Governance Vacuum: There is no international treaty or binding framework governing the development or deployment of offensive-capable AI models, or regulating dual-use AI systems.
- Transparency: Only limited information has been publicly disclosed about the vulnerabilities identified by Mythos. Questions arise whether such disclosures are fully driven by safety concerns or influenced by commercial interests.
UPSC Mains PYQ 2023
Q. Introduce the concept of Artificial Intelligence (AI). How does Al help clinical diagnosis? Do you perceive any threat to the privacy of the individual in the use of AI in healthcare?
Tell Google you want more of this.
Add Anantam IAS as a preferred sourceOne tap, and this site shows up more often in your own Top Stories, AI Overviews and AI Mode. Remove it any time.