Why in News?
The operationalisation of NATGRID (the National Intelligence Grid) is back in focus as a unified intelligence-sharing backbone that connects sensitive citizen databases for India’s security and intelligence agencies. Conceived in the aftermath of the 26/11 Mumbai attacks (2008), it is meant to give authorised users near-real-time, searchable access to scattered government data for counter-terror investigations.
Its roll-out has revived a sharp constitutional debate: the platform sits inside a country that still lacks a dedicated surveillance law, even after the Supreme Court recognised privacy as a fundamental right in Justice K.S. Puttaswamy (2017) and Parliament passed the Digital Personal Data Protection (DPDP) Act, 2023.
- NATGRID integrates roughly 21 databases spanning banking, telecom, immigration, travel, tax and other records.
- It was sanctioned in 2009-10 as a direct institutional response to intelligence failures around 26/11.
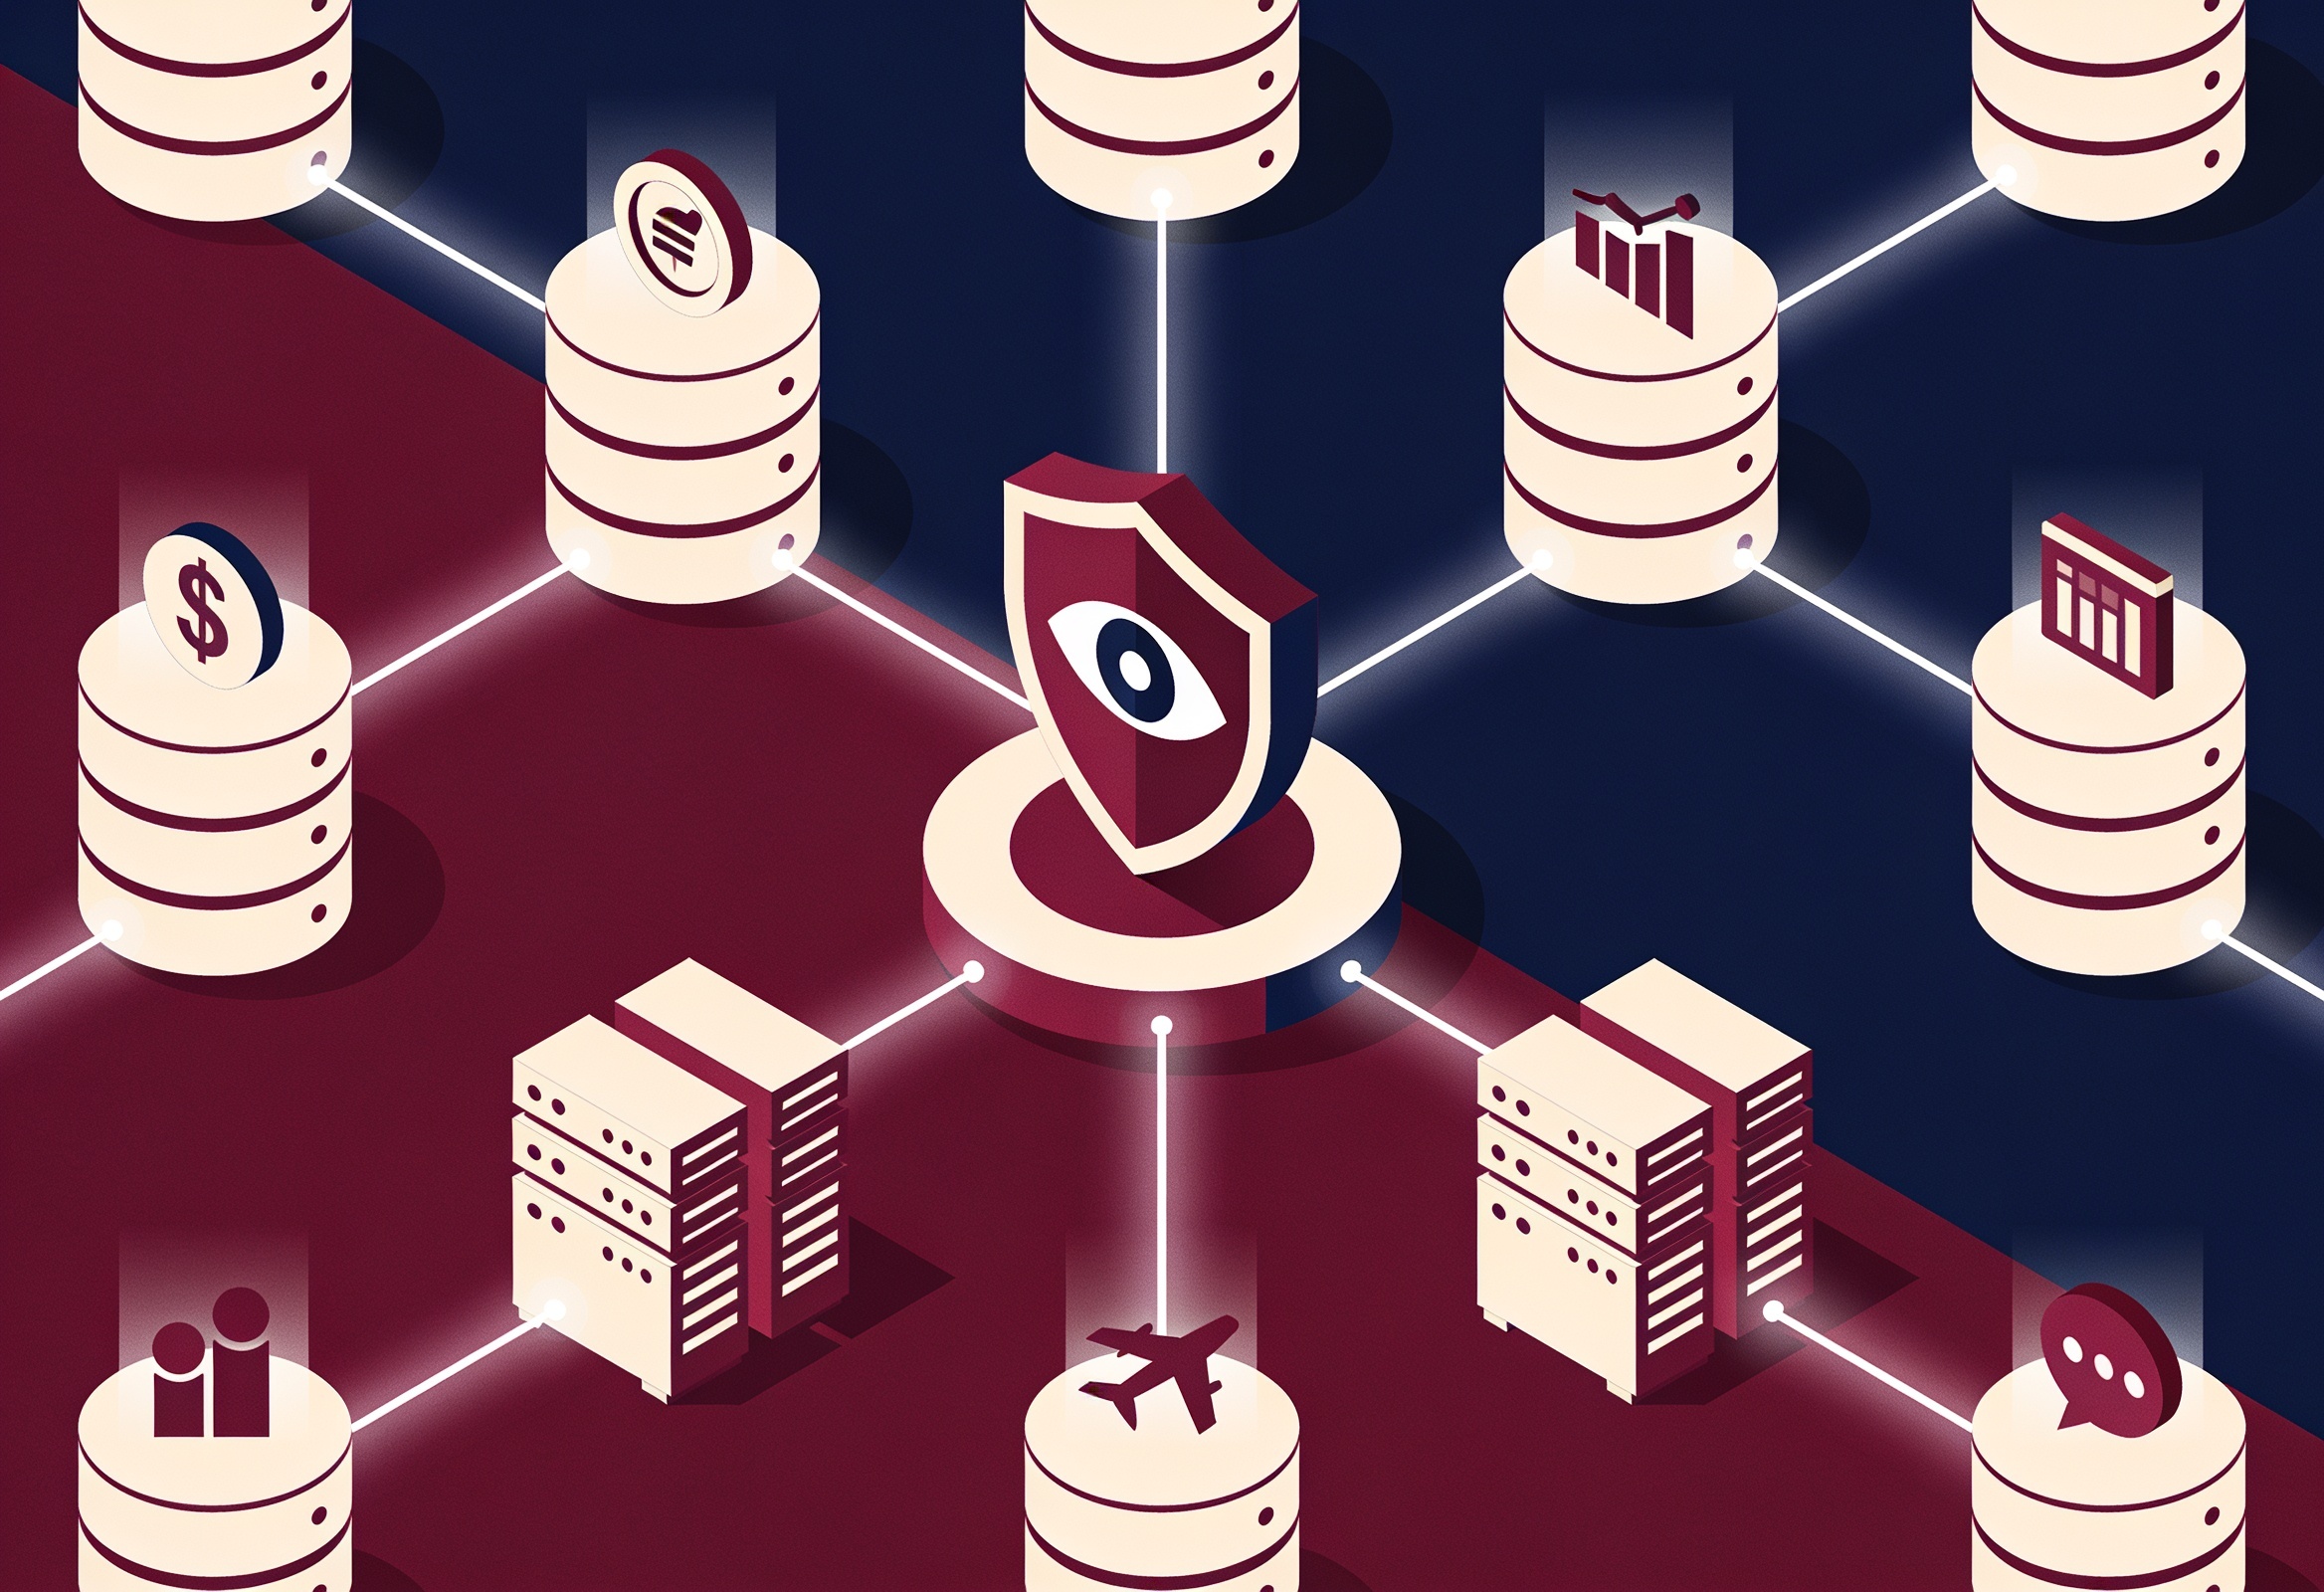
- It functions as a secure search-and-retrieval layer, not a new database — it queries existing data held by other agencies.
- Access is meant to be restricted to designated central security and intelligence agencies, not open-ended.
- The debate it triggers turns on the proportionality test laid down in Puttaswamy and the absence of standalone surveillance legislation.
The development matters in the context of:
- Matters because India’s counter-terror response depends on fusing data that today sits in silos across ministries and agencies.
- Matters because surveillance powers are still exercised under colonial-era and pre-internet statutes rather than a modern, rights-aware framework.
- Matters because the DPDP Act, 2023 grants the State broad exemptions, leaving the citizen-versus-state balance largely to executive discretion.
UPSC Relevance
Prelims Relevance
- NATGRID — National Intelligence Grid, under the Ministry of Home Affairs (MHA)
- Origin: institutional response to the 26/11 Mumbai attacks (2008)
- Links approximately 21 sensitive databases (banking, telecom, immigration, travel, tax)
- Justice K.S. Puttaswamy v. Union of India (2017) — right to privacy under Article 21
- The proportionality doctrine: legitimate aim, suitable means, necessity, balancing
- Digital Personal Data Protection (DPDP) Act, 2023 and State exemptions
- Interception powers: Section 5(2), Indian Telegraph Act, 1885 and Section 69, IT Act, 2000
- Related bodies: NIA, Intelligence Bureau (IB), R&AW, NCTC (proposed)
- CMS (Centralised Monitoring System) and NETRA — distinct surveillance projects
Mains Relevance
GS Paper 3
- Linkages between development and the spread of extremism; the role of an integrated intelligence grid in India’s internal-security architecture.
- Challenges to internal security through communication networks; the role of media and social networking sites; basics of cyber security and data protection.
GS Paper 2
- Government policies and interventions; the need for a dedicated surveillance/data-protection law and parliamentary oversight of intelligence agencies.
- Fundamental rights — the right to privacy as a facet of Article 21 and reasonable restrictions in the interest of security.
Essay
- Liberty and security are not opposites but conditions for each other.
- A surveillance State protects no one if it answers to no one.
Background and Context
What NATGRID is — and what it is not
NATGRID is a secure intelligence-sharing platform, not a fresh data-collection machine.
- It is a federated search-and-retrieval system that lets authorised agencies query data already held by other departments.
- It connects around 21 source databases — including banking, telecom, immigration, railway and air travel, and income-tax records.
- It does not create a new central pool of citizen data; it acts as a fast indexing-and-access layer over distributed silos.
- Access is designed to be limited to designated central security and intelligence agencies for counter-terror and security work.
- The goal is speed: turning days of inter-agency paperwork into a single authenticated query.
Why it was conceived — the 26/11 lesson
The grid is a structural fix for the intelligence fragmentation exposed by the 2008 attacks.
- The 26/11 Mumbai attacks revealed that critical leads lay scattered across agencies that did not share data in time.
- NATGRID was sanctioned in 2009-10 under the Ministry of Home Affairs to break those silos.
- It sits alongside other post-26/11 reforms within India’s internal security framework — the National Investigation Agency (NIA), coastal-security upgrades, and the proposed NCTC.
- The animating idea is intelligence fusion — connecting dots across financial, travel and communication footprints before an attack.
- Several states and agencies initially resisted, citing turf and the risk of a single point of data failure.
The constitutional anchor — Puttaswamy and proportionality
Any large-scale surveillance system must clear the bar the Supreme Court set in 2017.
- In Justice K.S. Puttaswamy v. Union of India (2017), a nine-judge bench held that the right to privacy is a fundamental right under Article 21.
- The court laid down a proportionality test: a legitimate State aim, a rational nexus, necessity (least-restrictive means), and a fair balance with rights.
- Surveillance must also satisfy legality — it needs the backing of a clear, publicly known law, not just executive instruction.
- The verdict implies that bulk or open-ended data access without safeguards is constitutionally suspect.
- Courts have since stressed procedural safeguards, independent review, and data-minimisation as conditions for lawful interception.
The legal vacuum — no dedicated surveillance law
India authorises interception under old statutes never written for an integrated data grid.
- Telephone interception rests on Section 5(2) of the Indian Telegraph Act, 1885 and its rules.
- Digital interception and monitoring rest on Section 69 of the Information Technology Act, 2000.
- Neither statute contemplates a federated grid linking financial, travel and communication records at scale.
- There is no standalone law that defines who may be surveilled, on what threshold, with what judicial or parliamentary oversight.
- Critics argue this leaves NATGRID-type access governed largely by executive discretion and internal guidelines.
DPDP Act 2023 — protection with broad State exemptions
The data-protection law tightens private-sector rules but carves out wide space for the State.
- The Digital Personal Data Protection (DPDP) Act, 2023 is India’s first horizontal data-protection statute.
- It allows the Central Government to exempt notified agencies from the Act’s obligations on grounds such as sovereignty, integrity and security of the State.
- These exemptions can switch off consent, purpose-limitation and data-minimisation duties for security agencies.
- The Act does not create an independent surveillance oversight body or judicial warrant requirement.
- So the citizen-versus-State balance is shaped less by hard statutory limits and more by how exemptions are written and used.
Security gains versus privacy risks
The grid promises faster counter-terror action but concentrates power over sensitive data.
- Security upside: rapid intelligence fusion, quicker tracing of suspects, fewer fatal delays in fast-moving plots.
- Privacy risk: profiling and function creep, where a counter-terror tool drifts into routine monitoring.
- Governance risk: weak audit trails and the absence of independent review invite misuse or chilling effects on dissent.
- Security risk: a high-value, integrated access layer is itself an attractive target for breaches and insider threats.
- Trust risk: opacity around who queries what, and when, erodes public confidence in the State’s restraint.
Way Forward
Enact a dedicated surveillance law
- Replace the patchwork of 1885 and 2000 statutes with a modern, rights-aware surveillance framework.
- Codify clear thresholds, time limits, and a least-restrictive-means requirement consistent with Puttaswamy.
Build independent oversight
- Introduce judicial or quasi-judicial authorisation for access to sensitive linked data.
- Create a standing parliamentary intelligence-oversight committee, as in many democracies.
Engineer privacy into the system
- Apply data-minimisation, purpose-limitation and tamper-proof audit logs by design.
- Mandate periodic independent security and privacy audits, with summary findings placed before Parliament.
Conclusion
NATGRID answers a real and proven need: the 26/11 failure to connect intelligence in time cost lives, and a federated grid can close that gap. The question is not whether the State should fuse intelligence, but on what terms — and who watches the watchers.
The Puttaswamy framework and the DPDP Act, 2023 give India the constitutional vocabulary; what is missing is a dedicated surveillance law, independent oversight, and privacy-by-design. Get those right, and security and liberty reinforce rather than cancel each other.
UPSC Practice Questions
Prelims MCQ 1
With reference to NATGRID (National Intelligence Grid), consider the following statements:
- It was conceived as an institutional response in the aftermath of the 26/11 Mumbai attacks.
- It functions primarily as a single new central database that collects citizen information directly from the public.
- It is meant to link multiple existing government databases such as banking, telecom and immigration records.
How many of the above statements are correct?
(a) Only one (b) Only two (c) All three (d) None
Answer: (b) Only two
Explanation:
Statements 1 and 3 are correct. Statement 2 is wrong — NATGRID is a secure search-and-retrieval layer over existing databases, not a fresh central data-collection pool.
Prelims MCQ 2
The proportionality test for restricting the right to privacy was authoritatively laid down by the Supreme Court in which case?
(a) Maneka Gandhi v. Union of India (1978) (b) Kesavananda Bharati v. State of Kerala (1973) (c) Justice K.S. Puttaswamy v. Union of India (2017) (d) Shreya Singhal v. Union of India (2015)
Answer: (c) Justice K.S. Puttaswamy v. Union of India (2017)
Explanation:
The nine-judge bench in Puttaswamy (2017) held privacy to be a fundamental right under Article 21 and set out the proportionality test for State restrictions.
UPSC Mains Questions
- NATGRID was conceived to fuse intelligence after 26/11, yet India still lacks a dedicated surveillance law. Examine the constitutional and governance challenges of operating such an intelligence grid in light of the Puttaswamy judgment. (250 words)
- “Security and privacy are not rival claims but interdependent goods.” Critically analyse this statement with reference to India’s surveillance architecture and the Digital Personal Data Protection Act, 2023. (250 words)
- Discuss the case for independent oversight of intelligence agencies in India. What institutional safeguards would make data-integration systems like NATGRID compatible with fundamental rights? (150 words)
Sources: Ministry of Home Affairs, Government of India and Press Information Bureau.
Frequently Asked Questions
What is NATGRID in simple terms?
NATGRID, the National Intelligence Grid, is a secure platform under the Ministry of Home Affairs that lets authorised security and intelligence agencies quickly search data already held across various government departments. It links roughly 21 databases, such as banking, telecom and travel records, to support counter-terror investigations rather than creating a brand-new central database of its own.
Why was NATGRID created?
It was conceived after the 26/11 Mumbai attacks of 2008, which exposed how critical intelligence leads were scattered across agencies that did not share information in time. Sanctioned around 2009-10, NATGRID was designed to break these data silos and enable faster intelligence fusion, so that financial, travel and communication footprints could be connected before, not after, an attack.
Which databases does NATGRID link?
It connects approximately 21 sensitive source databases. These include banking and financial records, telecom data, immigration and visa records, railway and air-travel bookings, and income-tax information, among others. NATGRID does not own this data; it queries the systems that already hold it, acting as a fast, authenticated access-and-indexing layer for designated central agencies.
How does the right to privacy affect NATGRID?
In Justice K.S. Puttaswamy v. Union of India (2017), the Supreme Court held that privacy is a fundamental right under Article 21. Any surveillance or data-integration system must then pass a proportionality test — pursuing a legitimate aim, using the least-restrictive means, and balancing security against individual rights — and rest on a clear, publicly known law.
Does the DPDP Act 2023 cover surveillance by the State?
The Digital Personal Data Protection Act, 2023 governs how personal data is handled, but it allows the Central Government to exempt notified agencies on grounds like the security of the State. These exemptions can switch off consent and data-minimisation duties for security agencies, and the Act does not create an independent surveillance oversight body or a warrant requirement.
Why do critics worry about surveillance in India?
Critics point out that India authorises interception under old laws — Section 5(2) of the Indian Telegraph Act, 1885 and Section 69 of the IT Act, 2000 — that were never written for an integrated data grid. With no dedicated surveillance law and limited independent oversight, they fear function creep, profiling, and a chilling effect on free expression and dissent.
Tell Google you want more of this.
Add Anantam IAS as a preferred sourceOne tap, and this site shows up more often in your own Top Stories, AI Overviews and AI Mode. Remove it any time.