Why in News?
The growing use of AI-powered smart glasses, equipped with discreet cameras, microphones and speakers, has raised concerns over non-consensual recording, biometric surveillance and misuse of personal data.
Unlike smartphones, these devices can record continuously without attracting attention, making traditional ideas of notice and consent increasingly inadequate.
| UPSC Relevance: GS-2 Polity and Governance: Fundamental Rights, Data protection; GS-3 Science and Technology: AI, cybersecurity and emerging technologies; GS-4 Ethics: Privacy, consent and corporate accountability Prelims: DPDP Act, 2023, Right to Privacy, IT Act, 2000, Data Protection Board Mains: Technology-law gap, Privacy in public spaces, Regulation of AI-enabled wearables |
What are Smart Glasses?
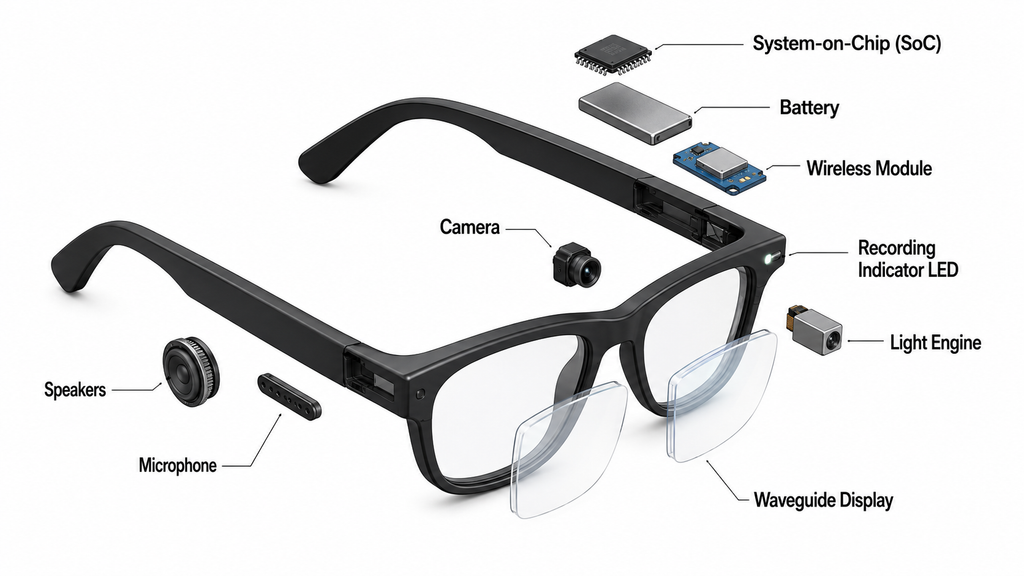
Smart glasses combine conventional eyewear with digital capabilities such as:
- Cameras and microphones for hands-free recording
- Voice assistants, calls, messaging and music
- AI-based translation, navigation and object recognition
- Cloud connectivity and real-time content sharing; and
- Potential facial recognition and augmented-reality applications.
They can improve accessibility for persons with disabilities, industrial productivity, navigation, education and emergency response.
However, their inconspicuous design also converts ordinary eyewear into a potentially continuous surveillance device.
Major Privacy and Ethical Concerns:
- Consent asymmetry: Manufacturers may give control to the wearer, but persons appearing in the frame generally receive no meaningful notice or opportunity to consent. Small LEDs or shutter sounds are inadequate in crowded and noisy spaces and may be obscured or circumvented.
- Privacy does not disappear in public: In K.S. Puttaswamy v. Union of India (2017), the Supreme Court recognised privacy as a fundamental right arising primarily from Article 21. It subsequently reiterated that privacy attaches to the person, not merely to a private place. Thus, entry into a street, classroom or workplace does not amount to blanket consent to persistent recording, identification or profiling.
- Function creep: A recording initially made for personal convenience may later be uploaded to social media, analysed using facial recognition, combined with location and voice data, used for targeted advertising or profiling, or reviewed by third-party contractors.
- Disproportionate impact on vulnerable groups: Covert recording can facilitate voyeurism, stalking, sexual harassment, doxing and child sexual exploitation. NCRB recorded 3,678 cybercrime cases specifically targeting women in 2023, including 2,767 cases involving obscene or sexually explicit material.
- Sensitive institutional spaces: Smart glasses can inadvertently or deliberately capture:
- Medical records and patient consultations
- Confidential workplace documents
- Examination papers and classroom lectures
- Court proceedings
- Private conversations; and
- Copyright-protected performances and films.
The long battery life of such devices magnifies the scale of incidental data collection.
India’s Existing Legal Framework:
Digital Personal Data Protection Act, 2023:
- The DPDP Act is technology-neutral and covers digitally processed personal data relating to an identifiable individual. It provides for consent, purpose limitation, security safeguards, erasure and additional protection for children.
However, several gaps remain:
- Personal or domestic use exemption: Data processed by an individual purely for a personal or domestic purpose falls outside the Act. This may shield initial recording by an individual, though subsequent commercial processing by a platform may still be regulated.
- Bystander problem: Rights under the Act are difficult to exercise when people do not know that they have been recorded or which entity is processing their data.
- No separate category of sensitive personal data: The Act does not expressly impose differentiated protection for biometric, health or sexual data.
- Publicly available data: The exclusion applies only when data have been made public by the individual concerned or under a legal obligation. Merely being present in a public place does not automatically make one’s image “publicly available”.
- Phased implementation: As of August 2026, many substantive obligations relating to consent, data-fiduciary duties and individual rights are scheduled to become operational only in May 2027.
Other applicable laws:
- Section 66E, IT Act: Punishes capturing or transmitting images of a person’s private area without consent, but is narrower than a general prohibition on covert recording.
- Sections 67A and 67B, IT Act: Address sexually explicit electronic material and child sexual abuse material.
- Section 77, Bharatiya Nyaya Sanhita: Penalises watching, capturing, or sharing images of a woman engaged in a private act without her consent.
- POCSO Act: Criminalises using children for pornographic purposes and possessing or distributing such material.
These provisions address specific harmful outcomes but do not establish a comprehensive framework for routine, non-consensual recording in public or semi-public spaces.
Way Forward:
- Privacy-by-design: Require on-device processing, data minimisation, encrypted storage and automatic deletion by default.
- Tamper-proof signalling: Recording should activate a prominent, non-disableable light; blocking or disabling the indicator should automatically deactivate the camera.
- Bystander protection: Introduce default blurring or anonymisation of non-target individuals and accessible mechanisms for deletion and grievance redressal.
- Special protection for biometric data: Facial recognition and identity matching should require explicit consent or clear statutory authorisation.
- Risk-based regulation: Mandate Data Protection Impact Assessments and independent audits for wearable devices capable of persistent recording or biometric analysis.
- Restricted-use zones: Hospitals, schools, examination centres, courts, changing rooms and sensitive workplaces should be empowered to prohibit or regulate recording wearables.
- Consumer transparency: Manufacturers must disclose whether recordings are uploaded to the cloud, reviewed by humans or shared with third parties.
- Institutional capacity: Strengthen the Data Protection Board, cyber-forensic facilities and coordination among MeitY, CCPA, I4C and State police.
- Public awareness: Promote visible etiquette and social norms governing wearable cameras, similar to rules developed around CCTV and mobile photography.
A blanket ban on smart glasses would undermine beneficial innovation and may soon become technologically unworkable. The objective should be to regulate their capabilities and risks, not merely their physical form.
In the age of ambient AI, privacy protection must extend beyond the device user to the unseen bystander, ensuring that technological convenience does not normalise a society of permanent, invisible surveillance.
Tell Google you want more of this.
Add Anantam IAS as a preferred sourceOne tap, and this site shows up more often in your own Top Stories, AI Overviews and AI Mode. Remove it any time.