Why in News?
The NIA searched five locations in five states while investigating an alleged DDoS campaign against government websites during Operation Sindoor.
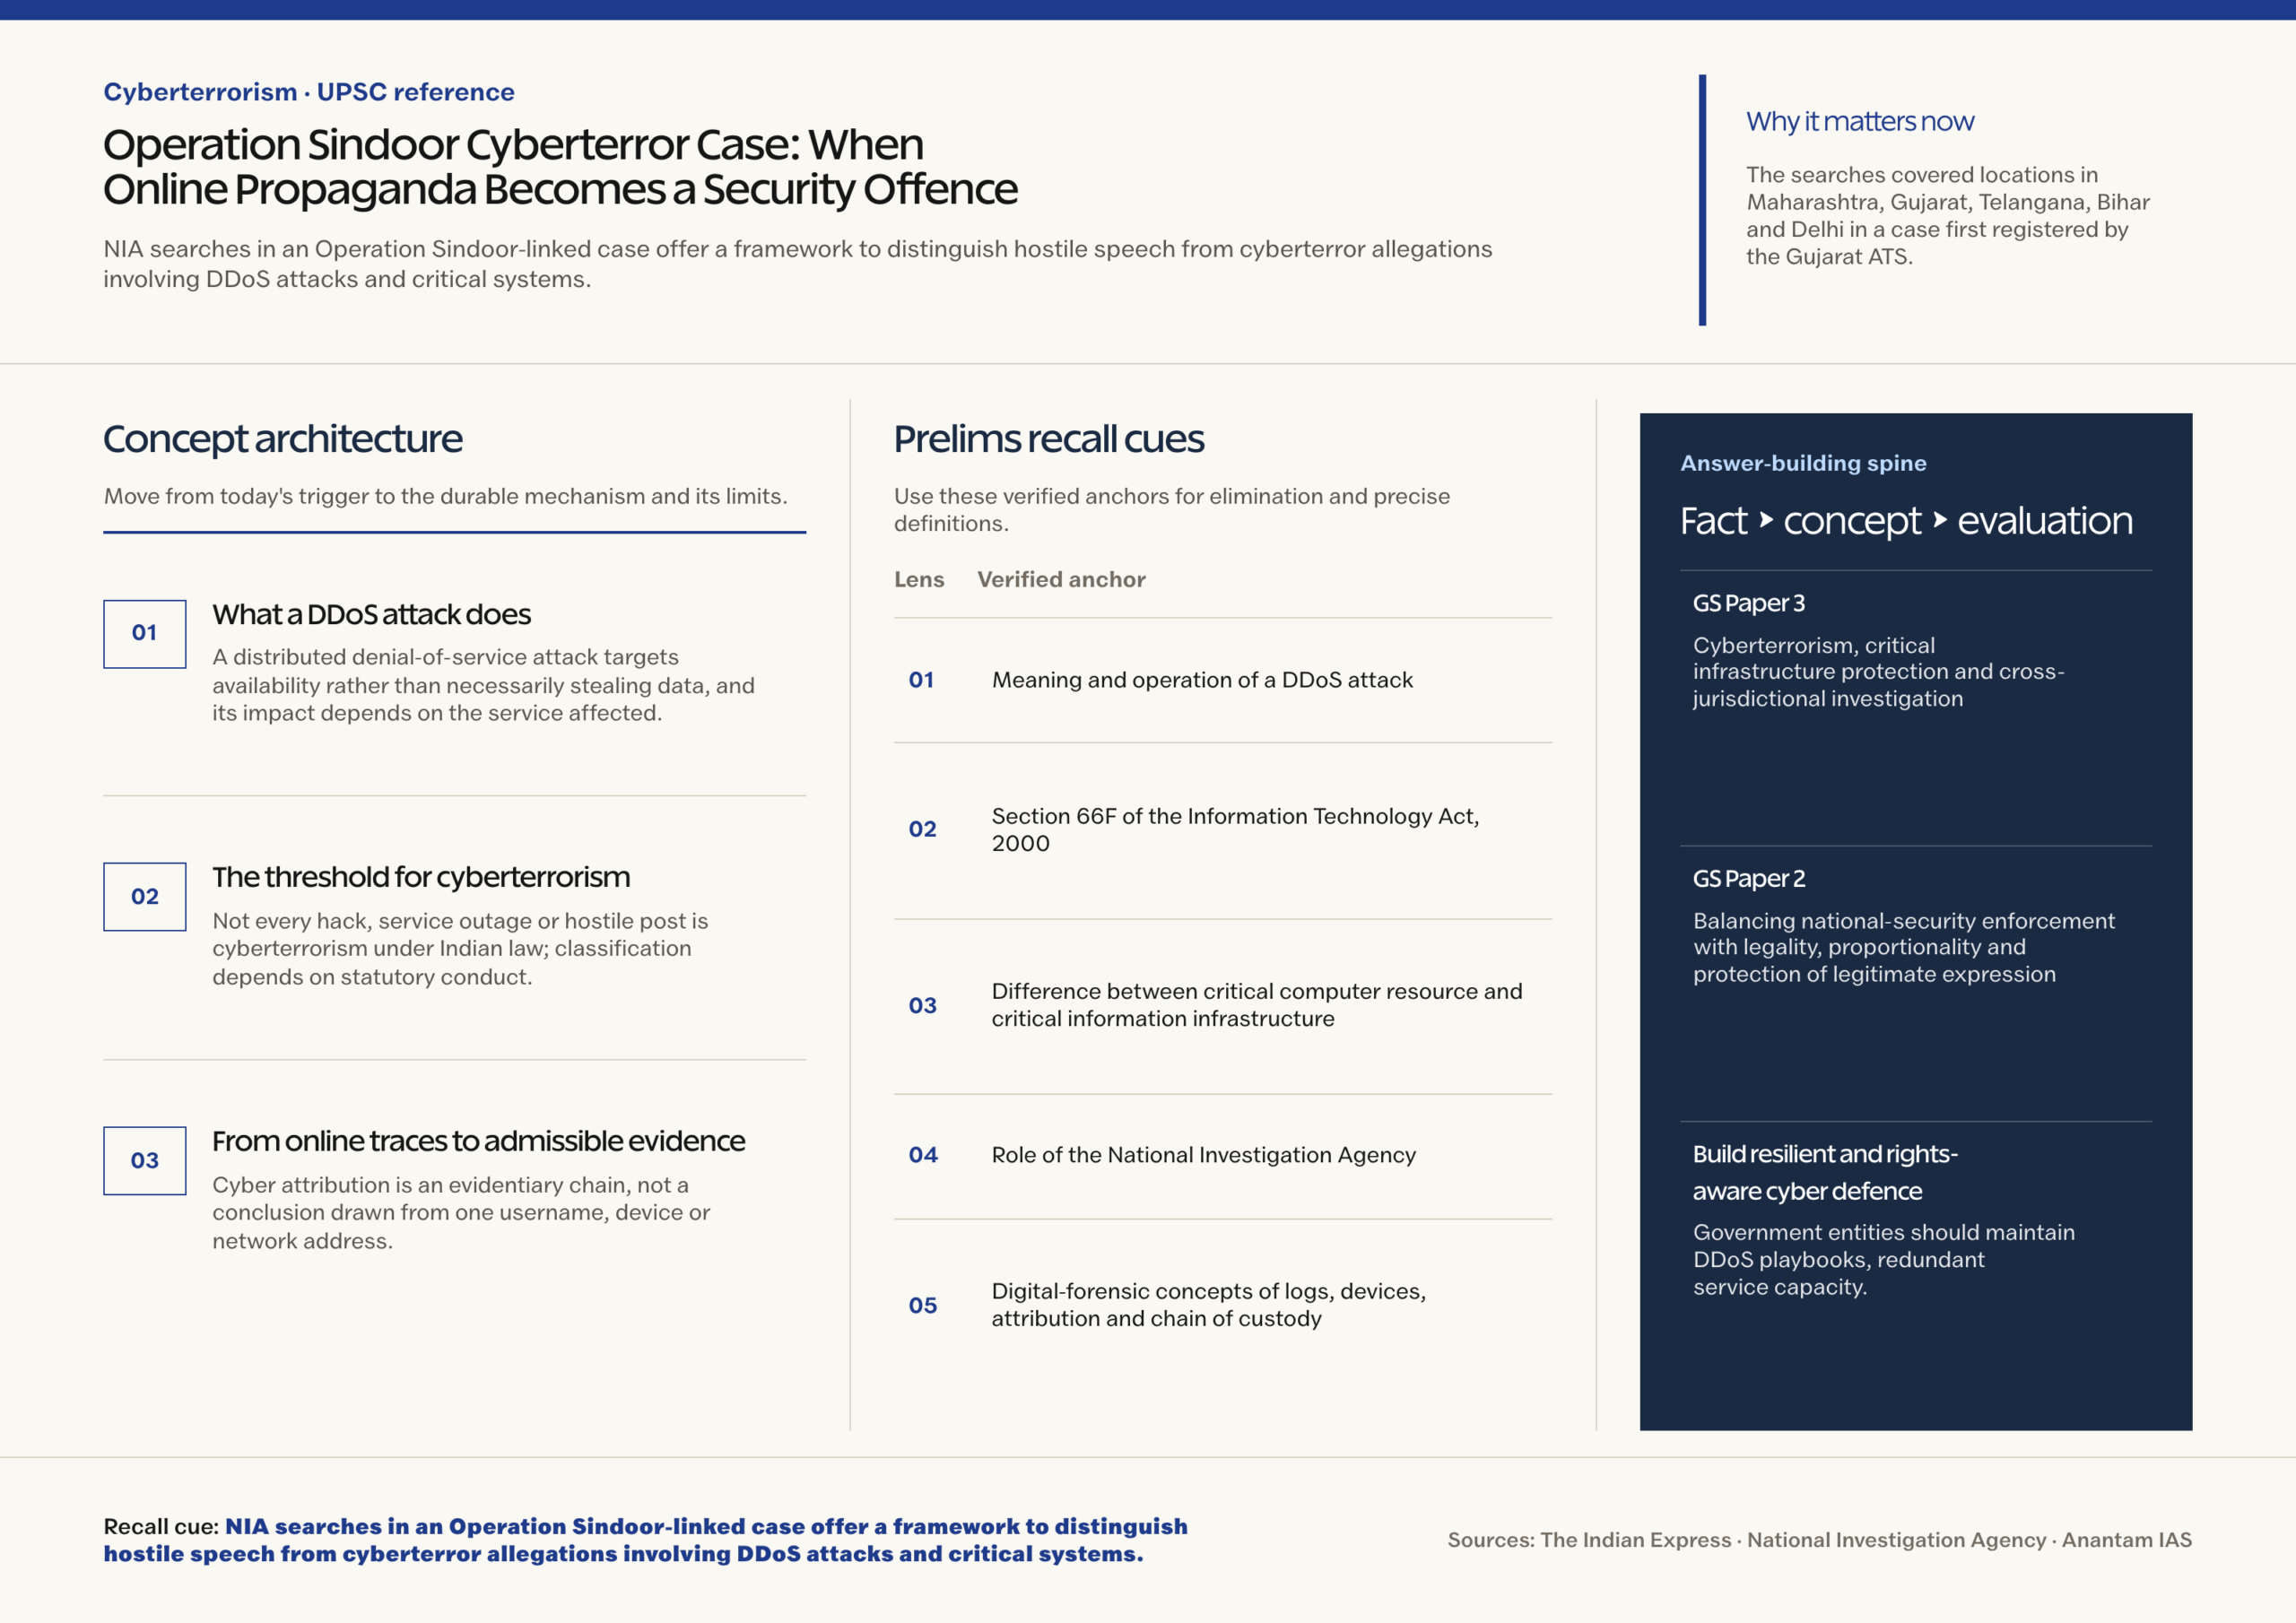
- The searches covered locations in Maharashtra, Gujarat, Telangana, Bihar and Delhi in a case first registered by the Gujarat ATS.
- The agency alleged an attempted DDoS attack against 54 government-entity websites, including critical computer resources and critical information infrastructure.
- Investigators said the searched suspects allegedly supported the accused in preparing for and improving skills used for the attacks.
- Digital devices and documents were seized for examination; the searches and seizures do not by themselves establish guilt.
- The case shows how an online act may move beyond objectionable content when it allegedly combines hostile intent with technical interference against protected systems.
- Attribution is difficult because distributed attacks can involve compromised devices, anonymising services, encrypted platforms and participants with different levels of knowledge.
UPSC Relevance
Prelims Relevance
- Meaning and operation of a DDoS attack
- Section 66F of the Information Technology Act, 2000
- Difference between critical computer resource and critical information infrastructure
- Role of the National Investigation Agency
- Digital-forensic concepts of logs, devices, attribution and chain of custody
Mains Relevance
GS Paper 3
- Cyberterrorism, critical infrastructure protection and cross-jurisdictional investigation
- DDoS capability, online coordination and evidentiary attribution
GS Paper 2
- Balancing national-security enforcement with legality, proportionality and protection of legitimate expression
Essay
- A resilient democracy must defend both its digital infrastructure and the legal distinctions that protect legitimate dissent.
Background and Context
What a DDoS attack does
A distributed denial-of-service attack targets availability rather than necessarily stealing data, and its impact depends on the service affected, duration and defensive capacity.
- Attackers direct traffic or requests from many sources toward a server, service or network until capacity is exhausted and legitimate users cannot obtain normal access.
- The distributed sources may include compromised devices in a botnet, making blocking and attribution harder than with a single-source attack launched from one address.
- A DDoS event can interrupt public services even when the attacker does not enter the underlying database, steal records or alter stored information.
- Attack traffic can target bandwidth, network protocols or application functions, so defenders must identify the exhausted layer before choosing an effective mitigation.
- Defenders use traffic filtering, rate limiting, distributed capacity and incident coordination, while investigators preserve server logs, provider records and configuration evidence.
The threshold for cyberterrorism
Not every hack, service outage or hostile post is cyberterrorism under Indian law; classification depends on statutory conduct, intended threat and the protected consequence.
- Section 66F of the IT Act links prohibited computer conduct with a specified terror-related intent and the consequence or likelihood described by the provision.
- Relevant intent includes threatening India’s unity, integrity, security or sovereignty, or striking terror among people or a section of people through the prohibited conduct.
- The provision covers certain unauthorised access, denial of access or introduction of computer contaminants where death, injury, property damage or essential-service disruption is caused or likely.
- Access to restricted information affecting security, sovereignty, friendly relations or specified protected interests can also enter the provision’s scope when its knowledge and intent conditions exist.
- Prosecution must prove the required conduct, connection, knowledge and intent; a political view or inflammatory message alone does not automatically satisfy every statutory element.
From online traces to admissible evidence
Cyber attribution is an evidentiary chain, not a conclusion drawn from one username, device or network address, because technical origin and human responsibility may differ.
- Investigators correlate forensic device images, server and network logs, account records, communications, payment trails and tool-use artefacts across a common, independently corroborated incident timeline.
- A device’s presence shows access or possession, but investigators must connect a person to control, knowledge and relevant acts, including preparation or assistance where alleged.
- VPNs, shared devices, compromised systems and false identities can obscure origin, requiring corroboration from independent technical, platform, provider and human evidence.
- A reliable chain of custody records how electronic material was collected, sealed, preserved, copied, analysed and produced, allowing integrity challenges to be tested.
- Court-authorised searches and forensic examination must remain tied to necessity, relevance and procedural safeguards, particularly when devices contain unrelated private information.
Way Forward
Build resilient and rights-aware cyber defence
- Government entities should maintain DDoS playbooks, redundant service capacity, tested escalation channels and coordinated reporting with sectoral and national incident-response bodies.
- Investigators need standard evidence-preservation requests and interoperable forensic procedures across states, platforms, service providers and affected departments.
- Charges should identify the specific act, protected resource, alleged consequence and required intent instead of collapsing propaganda, association and technical attack into one category.
- Capacity building should cover both advanced technical attribution and judicially reviewable documentation of how each accused person is linked to the alleged operation.
Conclusion
- Cyberterrorism analysis requires a three-part test: technical conduct, protected harm and terror-related intent; provocative online material may support an inference but cannot replace proof of those statutory elements.
- A strong Mains answer should pair infrastructure resilience, incident reporting and forensic cooperation with precise charging, individualised attribution, proportionality, judicial oversight and procedural safeguards.
UPSC Practice Questions
Prelims MCQ 1
With reference to Distributed Denial of Service attacks, consider the following statements:
- They commonly overwhelm a service with traffic from multiple sources.
- They necessarily involve theft of data from the target database.
- Compromised devices may be coordinated as a botnet.
How many of the above statements are correct?
(a) Only one (b) Only two (c) All three (d) None
Answer: (b) Only two
Explanation:
Statements 1 and 3 are correct. A DDoS attack targets service availability and does not necessarily involve data theft.
Prelims MCQ 2
Which provision of the Information Technology Act, 2000 specifically addresses cyberterrorism?
(a) Section 43 (b) Section 66C (c) Section 66F (d) Section 79
Answer: (c) Section 66F
Explanation:
Section 66F defines and punishes cyberterrorism, subject to its specified conduct, intent and consequence requirements.
UPSC Mains Questions
- Not every cyberattack or inflammatory online message amounts to cyberterrorism. Explain the legal and evidentiary thresholds that should guide such a determination.
- DDoS attacks expose both technical and institutional weaknesses in public digital infrastructure. Discuss a resilience strategy that also protects due process and legitimate expression.
Sources: The Indian Express and National Investigation Agency.
Frequently Asked Questions
What is a DDoS attack?
It is an attempt to make a server, service or network unavailable by flooding it with illegitimate traffic or requests from multiple, often compromised, sources.
Does every DDoS attack amount to cyberterrorism?
No. Cyberterrorism under Section 66F requires the specified computer conduct plus the provision’s intent and harm-related conditions; an ordinary service disruption does not automatically qualify.
What is critical information infrastructure?
It is a computer resource whose incapacitation or destruction would have a debilitating impact on national security, economy, public health or safety, under the IT Act framework.
Why is attribution difficult in a distributed attack?
Traffic may pass through compromised devices, shared systems, VPNs and false identities. Investigators must corroborate technical traces with evidence of control, knowledge, communication and intent.
Why does chain of custody matter for digital evidence?
It documents collection, preservation, copying, analysis and transfer of electronic material, helping a court assess whether the evidence remained authentic and unaltered.
Tell Google you want more of this.
Add Anantam IAS as a preferred sourceOne tap, and this site shows up more often in your own Top Stories, AI Overviews and AI Mode. Remove it any time.