Why in News?
The Central Industrial Security Force (CISF) said facial-recognition cameras at major airports will link to a proposed data fusion centre in Delhi, drawing in feeds from roughly 1.5 lakh surveillance cameras at vital installations and integrating with the National Intelligence Grid (NATGRID) for real-time monitoring. The Home Ministry has separately asked States to use a platform that reaches across driving licences, vehicle registrations, Aadhaar, airline records, bank data and suspicious-transaction reports.
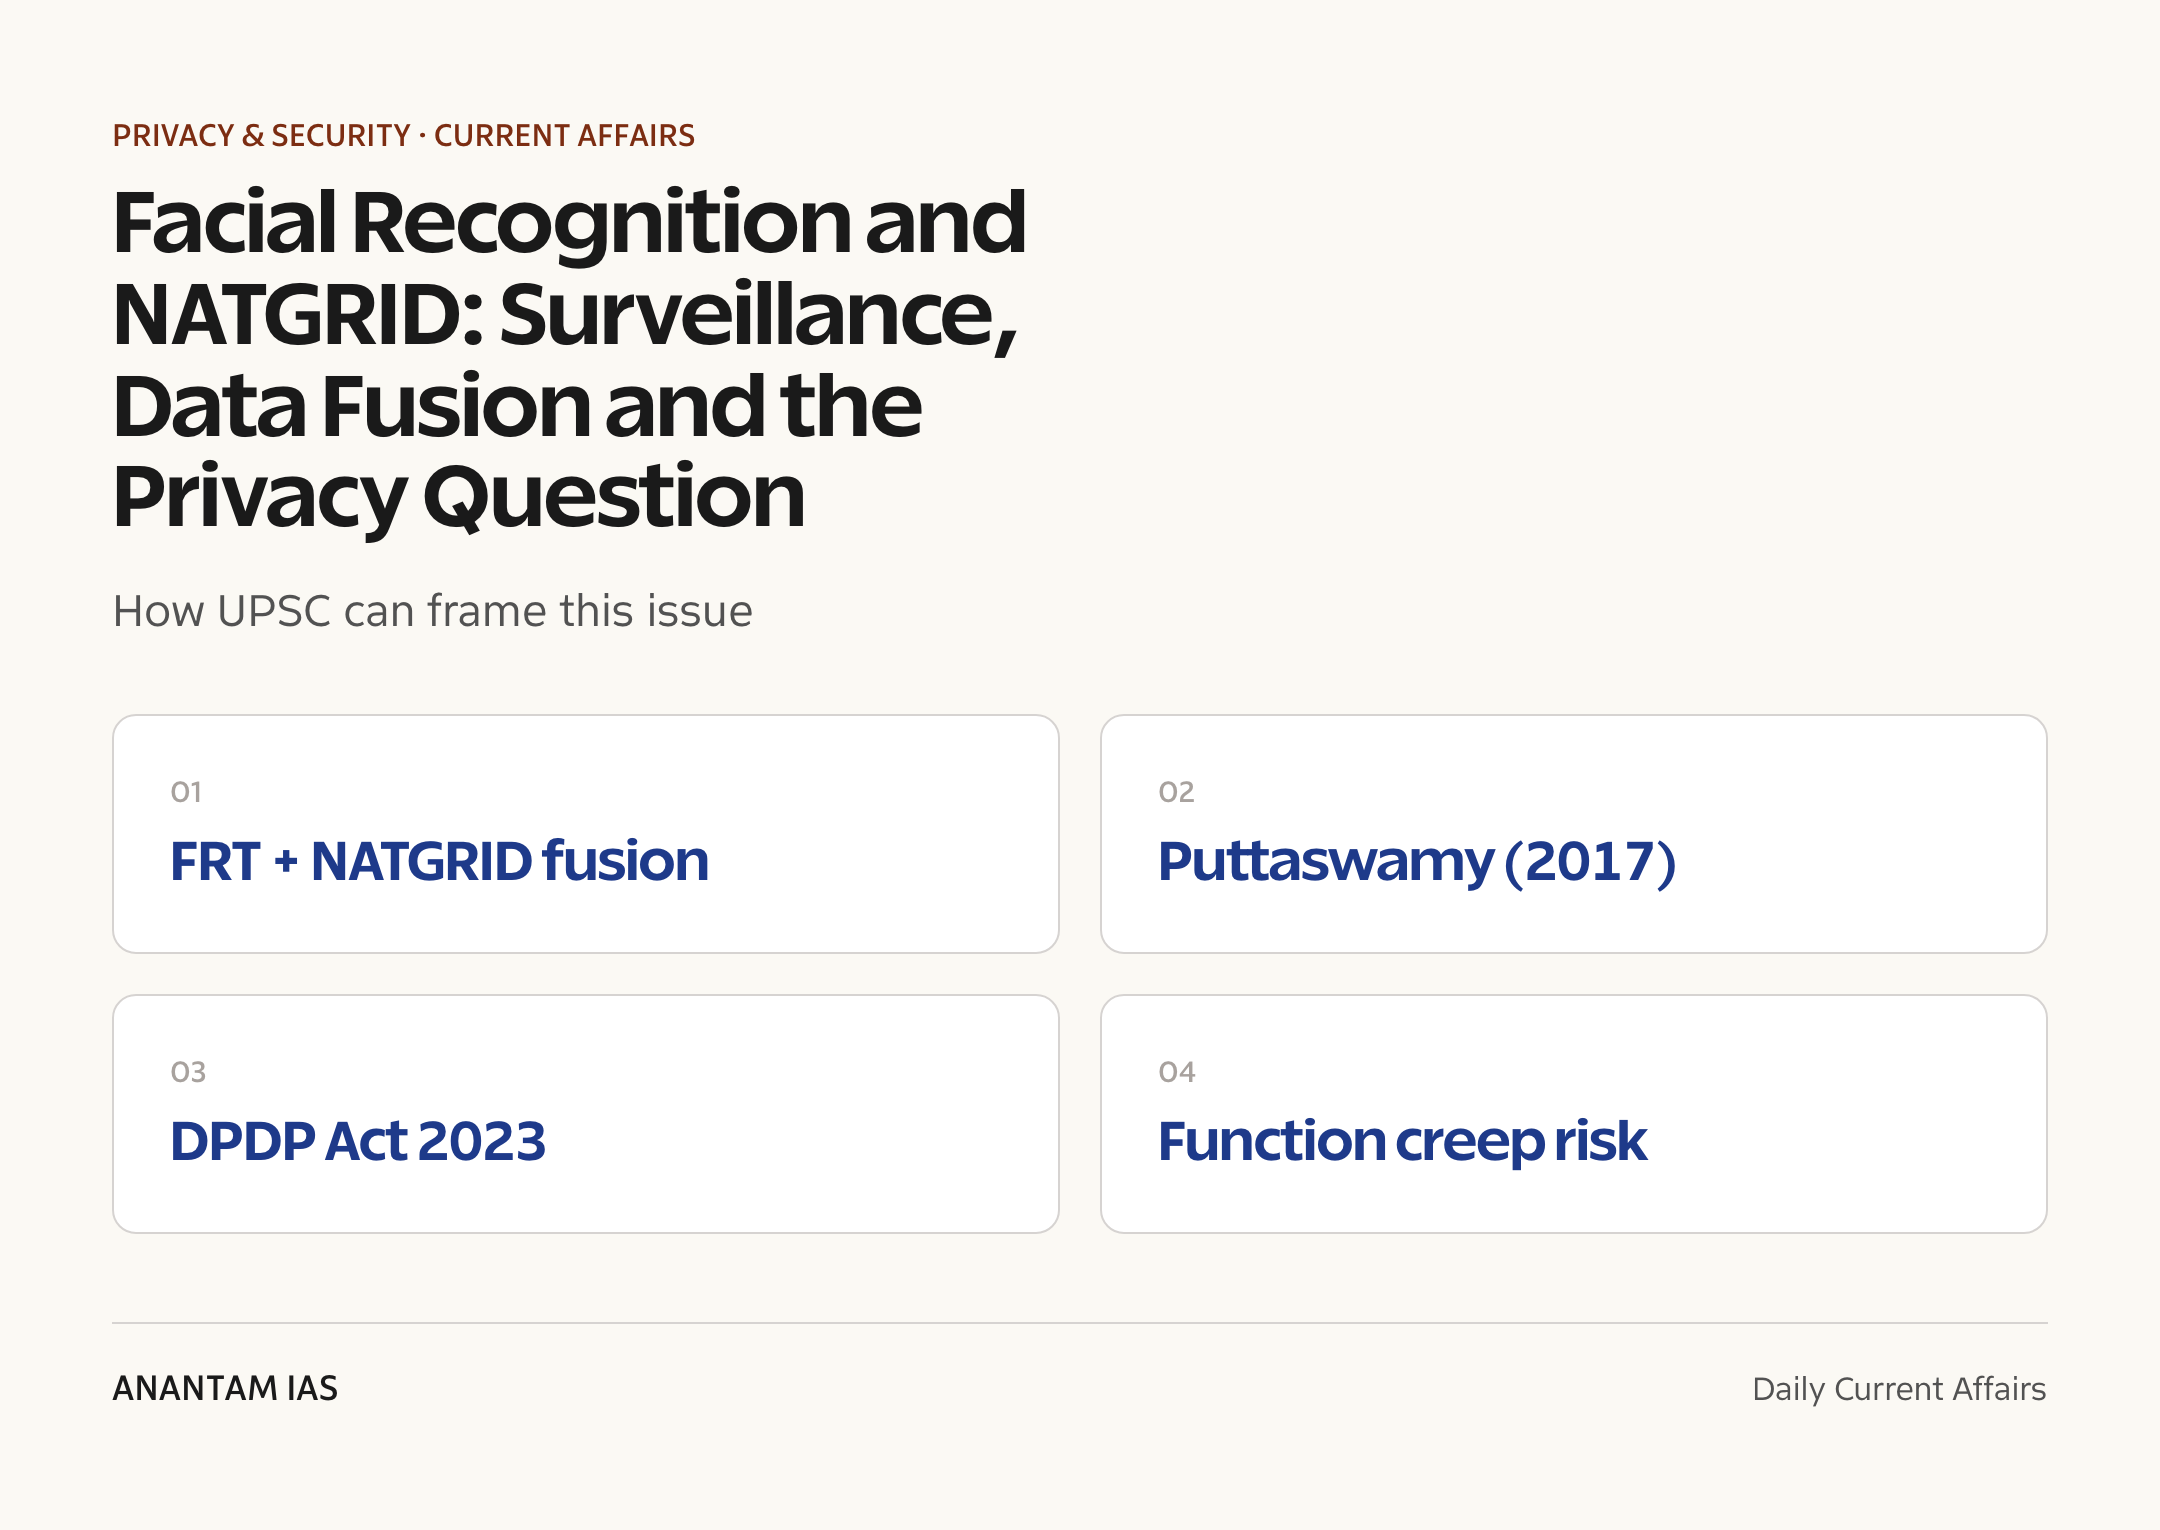
Reported by The Hindu (carried in the Legacy IAS daily analysis), the move revives a long-running debate. Pooling facial recognition technology (FRT) with NATGRID’s cross-dataset fusion gives security agencies powerful real-time identification, but it runs straight into the right to privacy affirmed in K.S. Puttaswamy (2017) and the safeguards expected under the Digital Personal Data Protection Act, 2023.
- CISF airport FRT cameras to feed a Delhi data fusion centre wired into NATGRID.
- Around 1.5 lakh cameras at vital installations to supply real-time feeds.
- Home Ministry platform spans licences, Aadhaar, airline, bank and transaction data plus social-media analysis.
- Complements a national DNA-and-biometric rollout under the Criminal Procedure (Identification) Act, 2022, with 100,000-plus DNA profiles via NAFIS.
- Raises the core test: do such systems satisfy legality, legitimate aim and proportionality under Puttaswamy.
The development matters in the context of:
- NATGRID was conceived after the 26/11 Mumbai attacks (2008) to break intelligence silos between agencies that had failed to connect actionable warnings.
- FRT is already used in policing, airport boarding through DigiYatra and crowd monitoring, but it still lacks a dedicated governing statute that defines who may deploy it and under what limits.
- India’s data-protection regime under the DPDP Act, 2023 is still being operationalised through subordinate rules and the setting up of a Data Protection Board.
- A fusion centre marks a shift from isolated cameras and registers to a single, queryable picture of a person’s movements, money and identity in one screen.
UPSC Relevance
Prelims Relevance
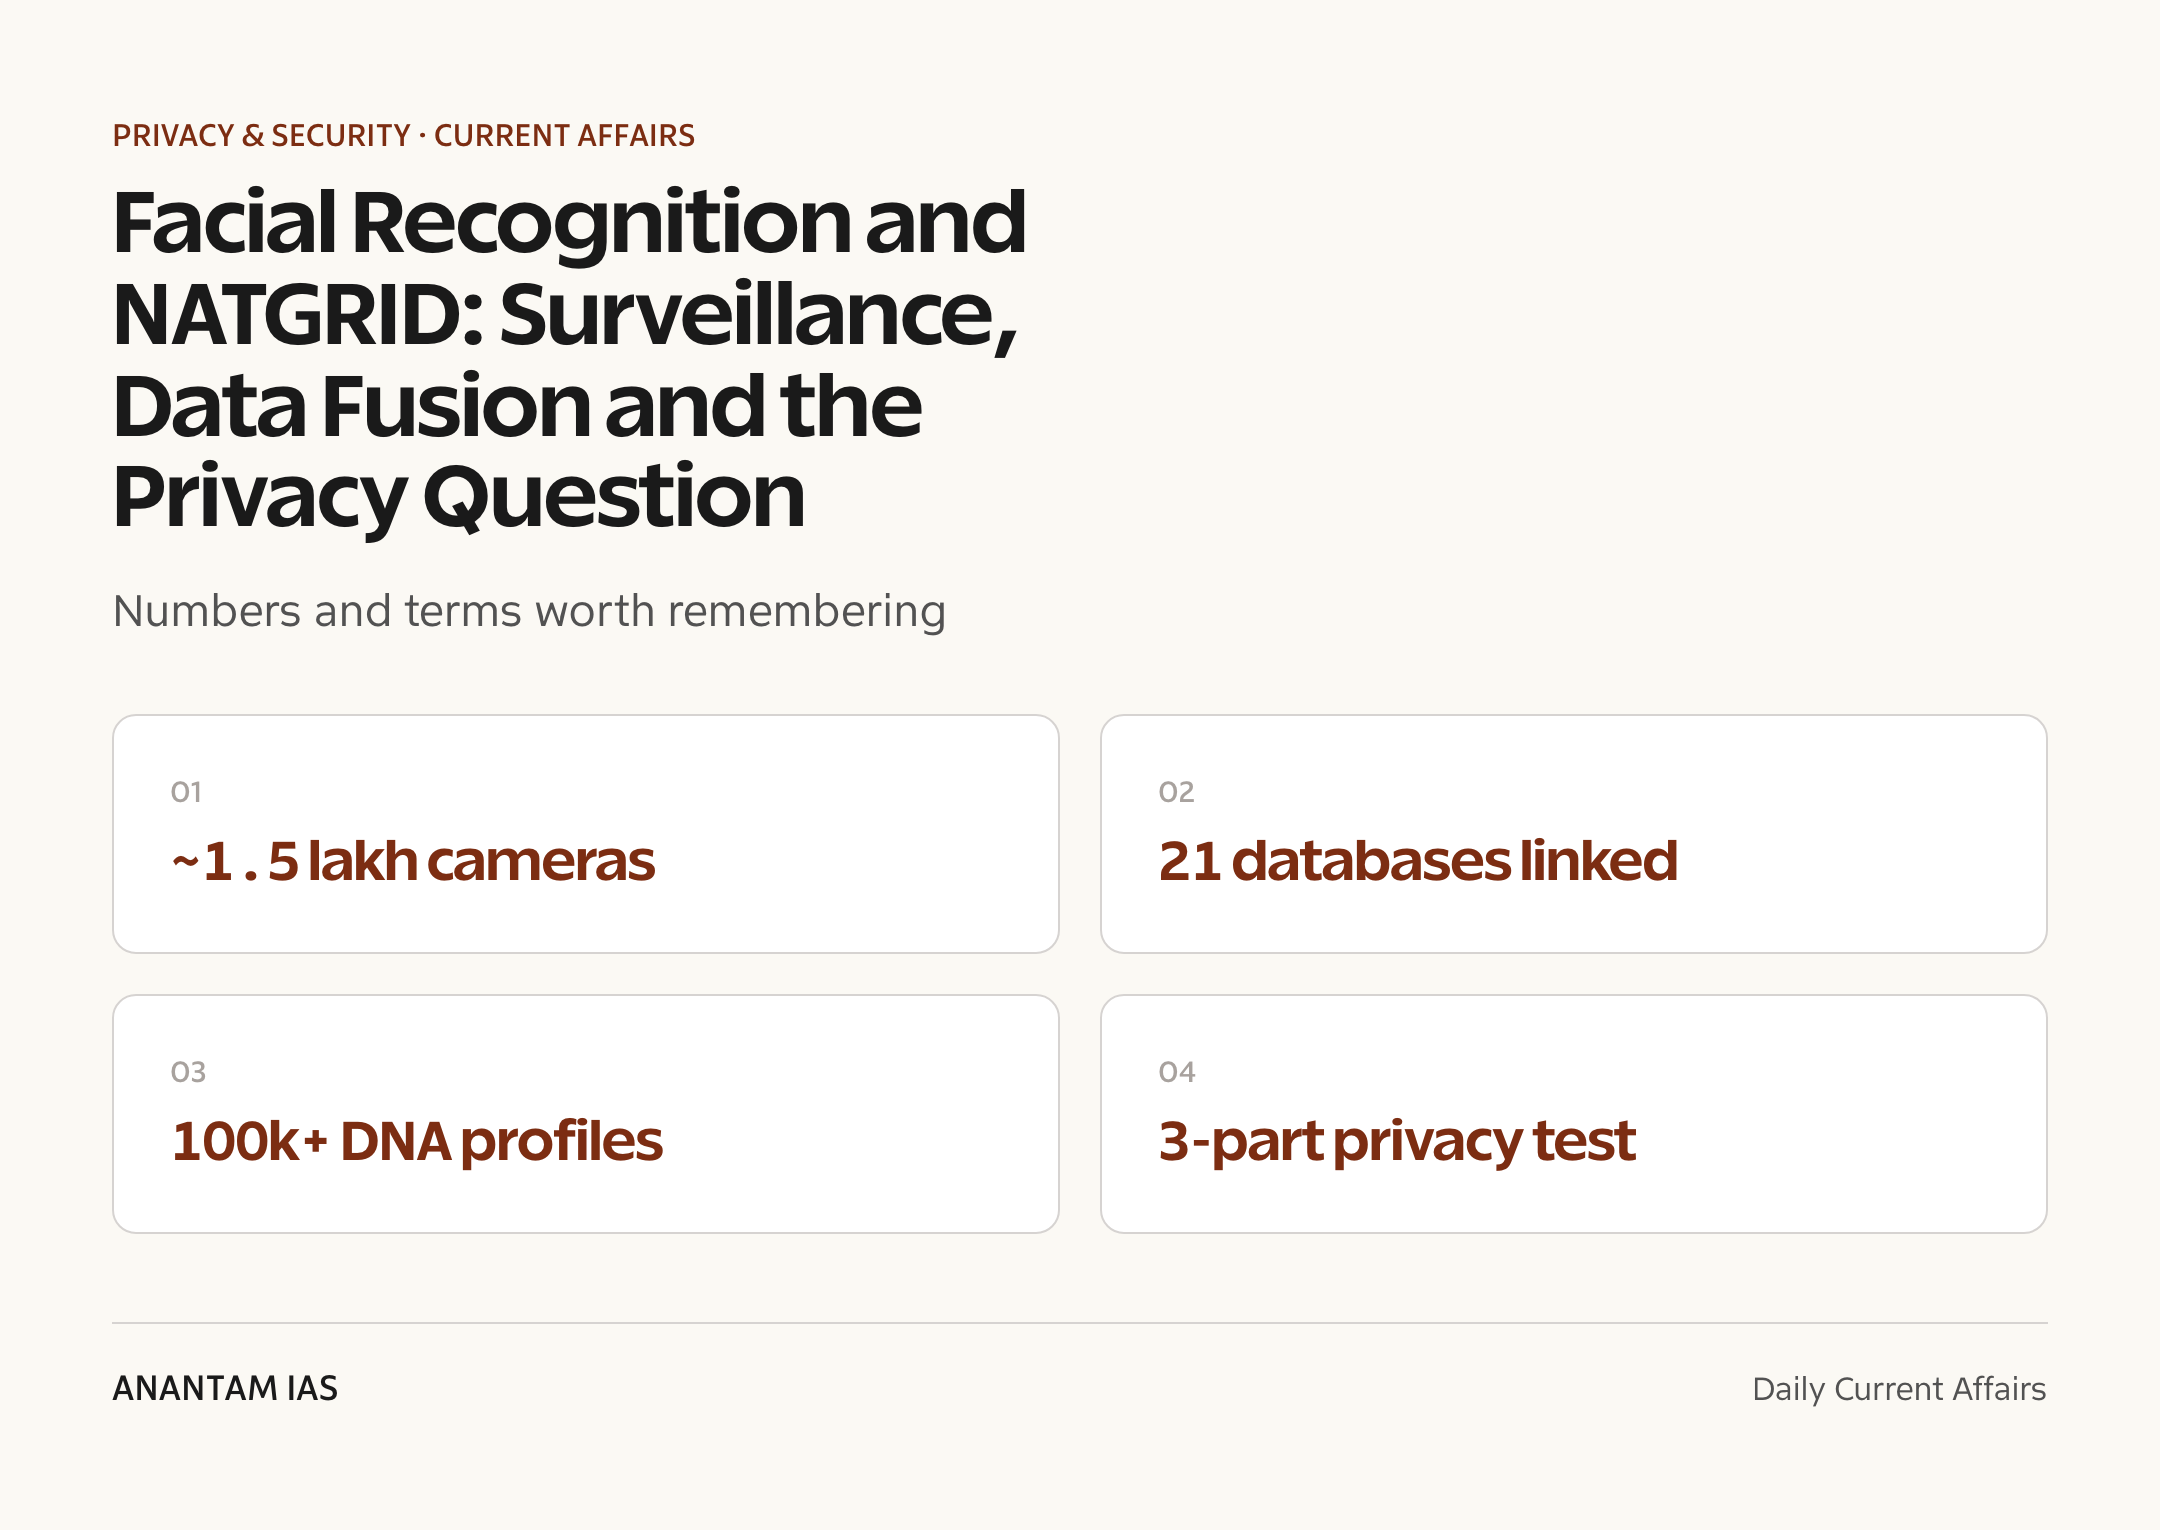
- NATGRID — National Intelligence Grid; links around 21 databases of multiple agencies; conceived post-26/11; attached to the Ministry of Home Affairs.
- K.S. Puttaswamy v. Union of India (2017) — nine-judge bench held privacy a fundamental right under Article 21; laid down the three-part proportionality test.
- Proportionality test limbs — legality (a valid law), legitimate/necessary aim, and proportionality (least-intrusive means, with procedural safeguards).
- DPDP Act, 2023 — first dedicated data-protection law; principles of purpose limitation, data minimisation, consent and a Data Protection Board of India.
- DPDP state exemptions — the Union may exempt State instrumentalities (Section 17) in the interest of sovereignty, security and public order.
- FRT — facial recognition technology; a biometric system matching face images against a database; prone to error rates and bias.
- Criminal Procedure (Identification) Act, 2022 — allows collection of biometric and biological samples; NAFIS is the fingerprint/criminal-record system.
- DigiYatra — facial-recognition-based contactless boarding at Indian airports.
- EU AI Act — classifies AI by risk tiers and restricts real-time remote biometric identification in public spaces.
Mains Relevance
GS Paper 2
- Right to privacy as a fundamental right (Article 21) and the limits it places on state surveillance.
- The Puttaswamy proportionality test as the constitutional yardstick for any data-fusion or FRT programme.
- Gaps in the DPDP Act 2023 — broad state exemptions and the independence of the Data Protection Board.
- Need for a clear legislative basis and judicial/parliamentary oversight of intelligence-grid surveillance.
GS Paper 3
- Internal-security utility of NATGRID and FRT in counter-terror, crowd control and border management.
- Risks of mass surveillance, profiling and function creep when datasets are fused without firewalls.
- Algorithmic bias and error rates in FRT, and the harm of false positives in policing.
- Cyber-security and data-breach exposure of a centralised fusion centre holding sensitive citizen data.
Essay
- Security versus liberty in the digital age — can the state watch without overreaching?
- Technology is a tool; its ethics depend on the safeguards we build around it.
Background and Context
FRT and NATGRID: what is being fused
The new architecture stitches biometric identification onto a long-planned intelligence grid, turning scattered feeds into one searchable system.
- Facial recognition technology (FRT) maps facial features into a numeric template and matches it against a stored gallery in near real time, flagging a name from a face in a crowd.
- NATGRID, conceived after 26/11, links roughly 21 databases so authorised agencies can query travel, financial and identity records in one place instead of writing to each department.
- The proposed data fusion centre in Delhi would combine airport FRT feeds, about 1.5 lakh installation cameras and NATGRID datasets into a single real-time monitoring layer.
- The Home Ministry platform reaches across driving licences, vehicle registrations, Aadhaar, airline, bank and suspicious-transaction data, with social-media analysis layered on top.
- It complements the DNA-and-biometric rollout under the Criminal Procedure (Identification) Act, 2022, which already holds 100,000-plus DNA profiles via the NAFIS criminal-records system.
- Each dataset alone is regulated loosely; the risk grows when they are joined, because the combined profile reveals far more than any single record.
The privacy jurisprudence: Puttaswamy
Any surveillance system in India must clear a constitutional gate set in 2017.
- K.S. Puttaswamy (2017), a nine-judge bench, held privacy intrinsic to life and liberty under Article 21 and treated informational autonomy as a protected interest.
- State intrusion must pass a three-part proportionality test: a backing law (legality), a legitimate and necessary aim, and the least-intrusive proportional means.
- The judgment also expects procedural safeguards against abuse — independent oversight, periodic review and limits on how long data is kept.
- Real-time identification and cross-dataset fusion, the analysis stresses, must satisfy legality, legitimate aim and proportionality rather than rest on administrative convenience.
- Mass, suspicion-less surveillance of the general public sits in tension with the proportionality limb, which favours targeted and least-intrusive measures.
DPDP Act 2023 and state exemptions
India’s data-protection statute sets principles but leaves wide room for the state.
- The DPDP Act, 2023 codifies purpose limitation, data minimisation, consent and storage-retention limits as the baseline for processing personal data.
- Compliance for these systems would demand purpose limitation, data minimisation, retention limits and independent oversight, the analysis notes.
- Section 17 lets the Union exempt State instrumentalities for sovereignty, integrity, security of the State and public order — a carve-out critics call broad and loosely defined.
- Exempted processing can sidestep core duties such as consent and purpose limitation, which is precisely where a fusion centre would operate.
- The Data Protection Board‘s independence, its appointment process and the absence of a dedicated surveillance-reform law remain open concerns.
Risks: function creep, bias and oversight gaps
Fusing datasets multiplies both capability and the scope for harm.
- Function creep — data gathered for one purpose drifts into others once silos are merged, a recurring concern in internal-security data systems.
- FRT carries documented error rates and demographic bias; false positives can wrongly implicate individuals, and the burden often falls on the person to disprove a machine’s match.
- A centralised fusion centre is a high-value cyber-attack and data-breach target, since a single compromise exposes linked identity, travel and financial records together.
- A chilling effect on free speech and assembly can follow when people know their movements are continuously tracked.
- The analysis warns of mass surveillance and profiling in the absence of strong institutional protections and independent oversight.
Global comparison
Other jurisdictions are tightening the leash on biometric surveillance.
- The EU AI Act sorts AI into risk tiers and curbs real-time remote biometric identification in public spaces.
- Several democracies require judicial authorisation or independent sign-off before deploying mass biometric tools.
- The contrast highlights India’s need for a statutory FRT framework rather than executive-led rollout.
Way Forward
Anchor any FRT or fusion-centre deployment in a clear law that names its purpose, scope and limits, as Puttaswamy requires.
Build in purpose limitation and data minimisation so datasets are not merged beyond the stated security aim.
Set strict retention and deletion timelines and audit logs for every query into the grid.
Create independent oversight — judicial or parliamentary review of surveillance powers, not executive self-certification.
Mandate bias and accuracy testing of FRT systems and publish error rates before operational use.
Narrow the DPDP Act’s state exemptions and strengthen the Data Protection Board’s autonomy.
Conclusion
NATGRID and facial recognition can sharpen India’s response to terror and organised crime, and the case for capable, real-time intelligence after 26/11 is genuine. The question is not whether the state may watch, but on what terms.
Puttaswamy and the DPDP Act already supply the grammar — legality, necessity, proportionality and oversight. Building these safeguards into the design, rather than bolting them on later, is what keeps a security tool from becoming an instrument of unchecked surveillance.
UPSC Practice Questions
Prelims MCQ 1
With reference to the National Intelligence Grid (NATGRID), consider the following statements: 1. It was conceived in the aftermath of the 26/11 Mumbai attacks. 2. It is designed to link databases of multiple agencies for security use. 3. It functions under the Ministry of Home Affairs. Which of the statements given above are correct?
1 and 2 only 2 and 3 only 1 and 3 only 1, 2 and 3
Answer: 1, 2 and 3
Explanation:
NATGRID was conceived after the 2008 Mumbai attacks to link around 21 databases of various agencies for security purposes and operates under the Ministry of Home Affairs.
Prelims MCQ 2
The three-part test of legality, legitimate aim and proportionality for limiting a fundamental right is most directly associated with which of the following?
The K.S. Puttaswamy (Right to Privacy) judgment, 2017 The Criminal Procedure (Identification) Act, 2022 The Digital Personal Data Protection Act, 2023 The Information Technology Act, 2000
Answer: The K.S. Puttaswamy (Right to Privacy) judgment, 2017
Explanation:
The 2017 Puttaswamy judgment recognised privacy as a fundamental right and laid down the three-part proportionality test for any state intrusion.
UPSC Mains Questions
- Cross-dataset fusion through systems like NATGRID enhances internal-security capability but strains the right to privacy. Examine in the light of the Puttaswamy proportionality test. (250 words)
- Facial recognition technology in public spaces raises concerns of function creep, algorithmic bias and mass surveillance. Suggest a regulatory framework that balances security with civil liberties. (250 words)
- “Data protection without independent oversight is a promise without a guarantee.” Critically evaluate the exemptions available to the state under the Digital Personal Data Protection Act, 2023. (150 words)
Source: The Hindu (via Legacy IAS analysis).
Frequently Asked Questions
What is NATGRID?
The National Intelligence Grid is a secure platform, conceived after the 26/11 attacks, that links around 21 databases of various agencies so authorised security users can access travel, financial and identity records in one place. It works under the Ministry of Home Affairs.
What did the Puttaswamy judgment decide?
The 2017 nine-judge K.S. Puttaswamy verdict held that the right to privacy is a fundamental right under Article 21. It also laid down a three-part test for any state intrusion: it must rest on a valid law, serve a legitimate and necessary aim, and be proportionate with procedural safeguards.
How does facial recognition technology work, and why is it controversial?
FRT converts a face into a digital template and matches it against a stored database in near real time. It is controversial because it can carry error rates and demographic bias, enable mass tracking, and is often deployed without a dedicated law or independent oversight.
What is function creep?
Function creep is when data collected for one stated purpose is gradually used for other, unrelated purposes. Fusing datasets that were once separate makes this drift far easier, which is why purpose limitation matters.
Does the DPDP Act 2023 limit government surveillance?
The Act sets principles such as purpose limitation, data minimisation and retention limits. However, Section 17 lets the Union exempt State instrumentalities in the interest of sovereignty, security and public order, which critics see as a broad carve-out.
How does the EU regulate biometric surveillance differently?
The EU AI Act classifies AI systems by risk and restricts real-time remote biometric identification in public spaces, often requiring strict conditions or authorisation. This contrasts with India’s largely executive-led FRT rollout.
Tell Google you want more of this.
Add Anantam IAS as a preferred sourceOne tap, and this site shows up more often in your own Top Stories, AI Overviews and AI Mode. Remove it any time.